Breach scenarios
Explore simulated incident situations in a dedicated platform.
SIMULATED BREACH INTELLIGENCE
Explore the scenario. Understand the risk.
ZelBreach is a simulated breach intelligence platform for exploring breach scenarios with synthetic data. It gives teams a dedicated environment to investigate scenario-based incident information.
Simulated breach intelligence
BUILT FOR YOUR WORKFLOW
Explore simulated incident situations in a dedicated platform.
Work with generated scenario data for investigation.
Review the context and relationships within a breach scenario.
THE COMPLETE PRODUCT GUIDE
Get to know the capabilities, workflows, and intelligence behind the product.
ZelBreach is a premium breach simulation platform built for security teams, architects, and leadership stakeholders who want a safer, clearer way to pressure-test readiness across identity, cloud, web, SaaS, endpoint, network, data, insider, and resilience use cases.
It combines environment modeling, crown-jewel awareness, ATT&CK coverage, defender control tuning, mission-control simulations, AI-assisted analysis, and rich reporting in one unified platform.
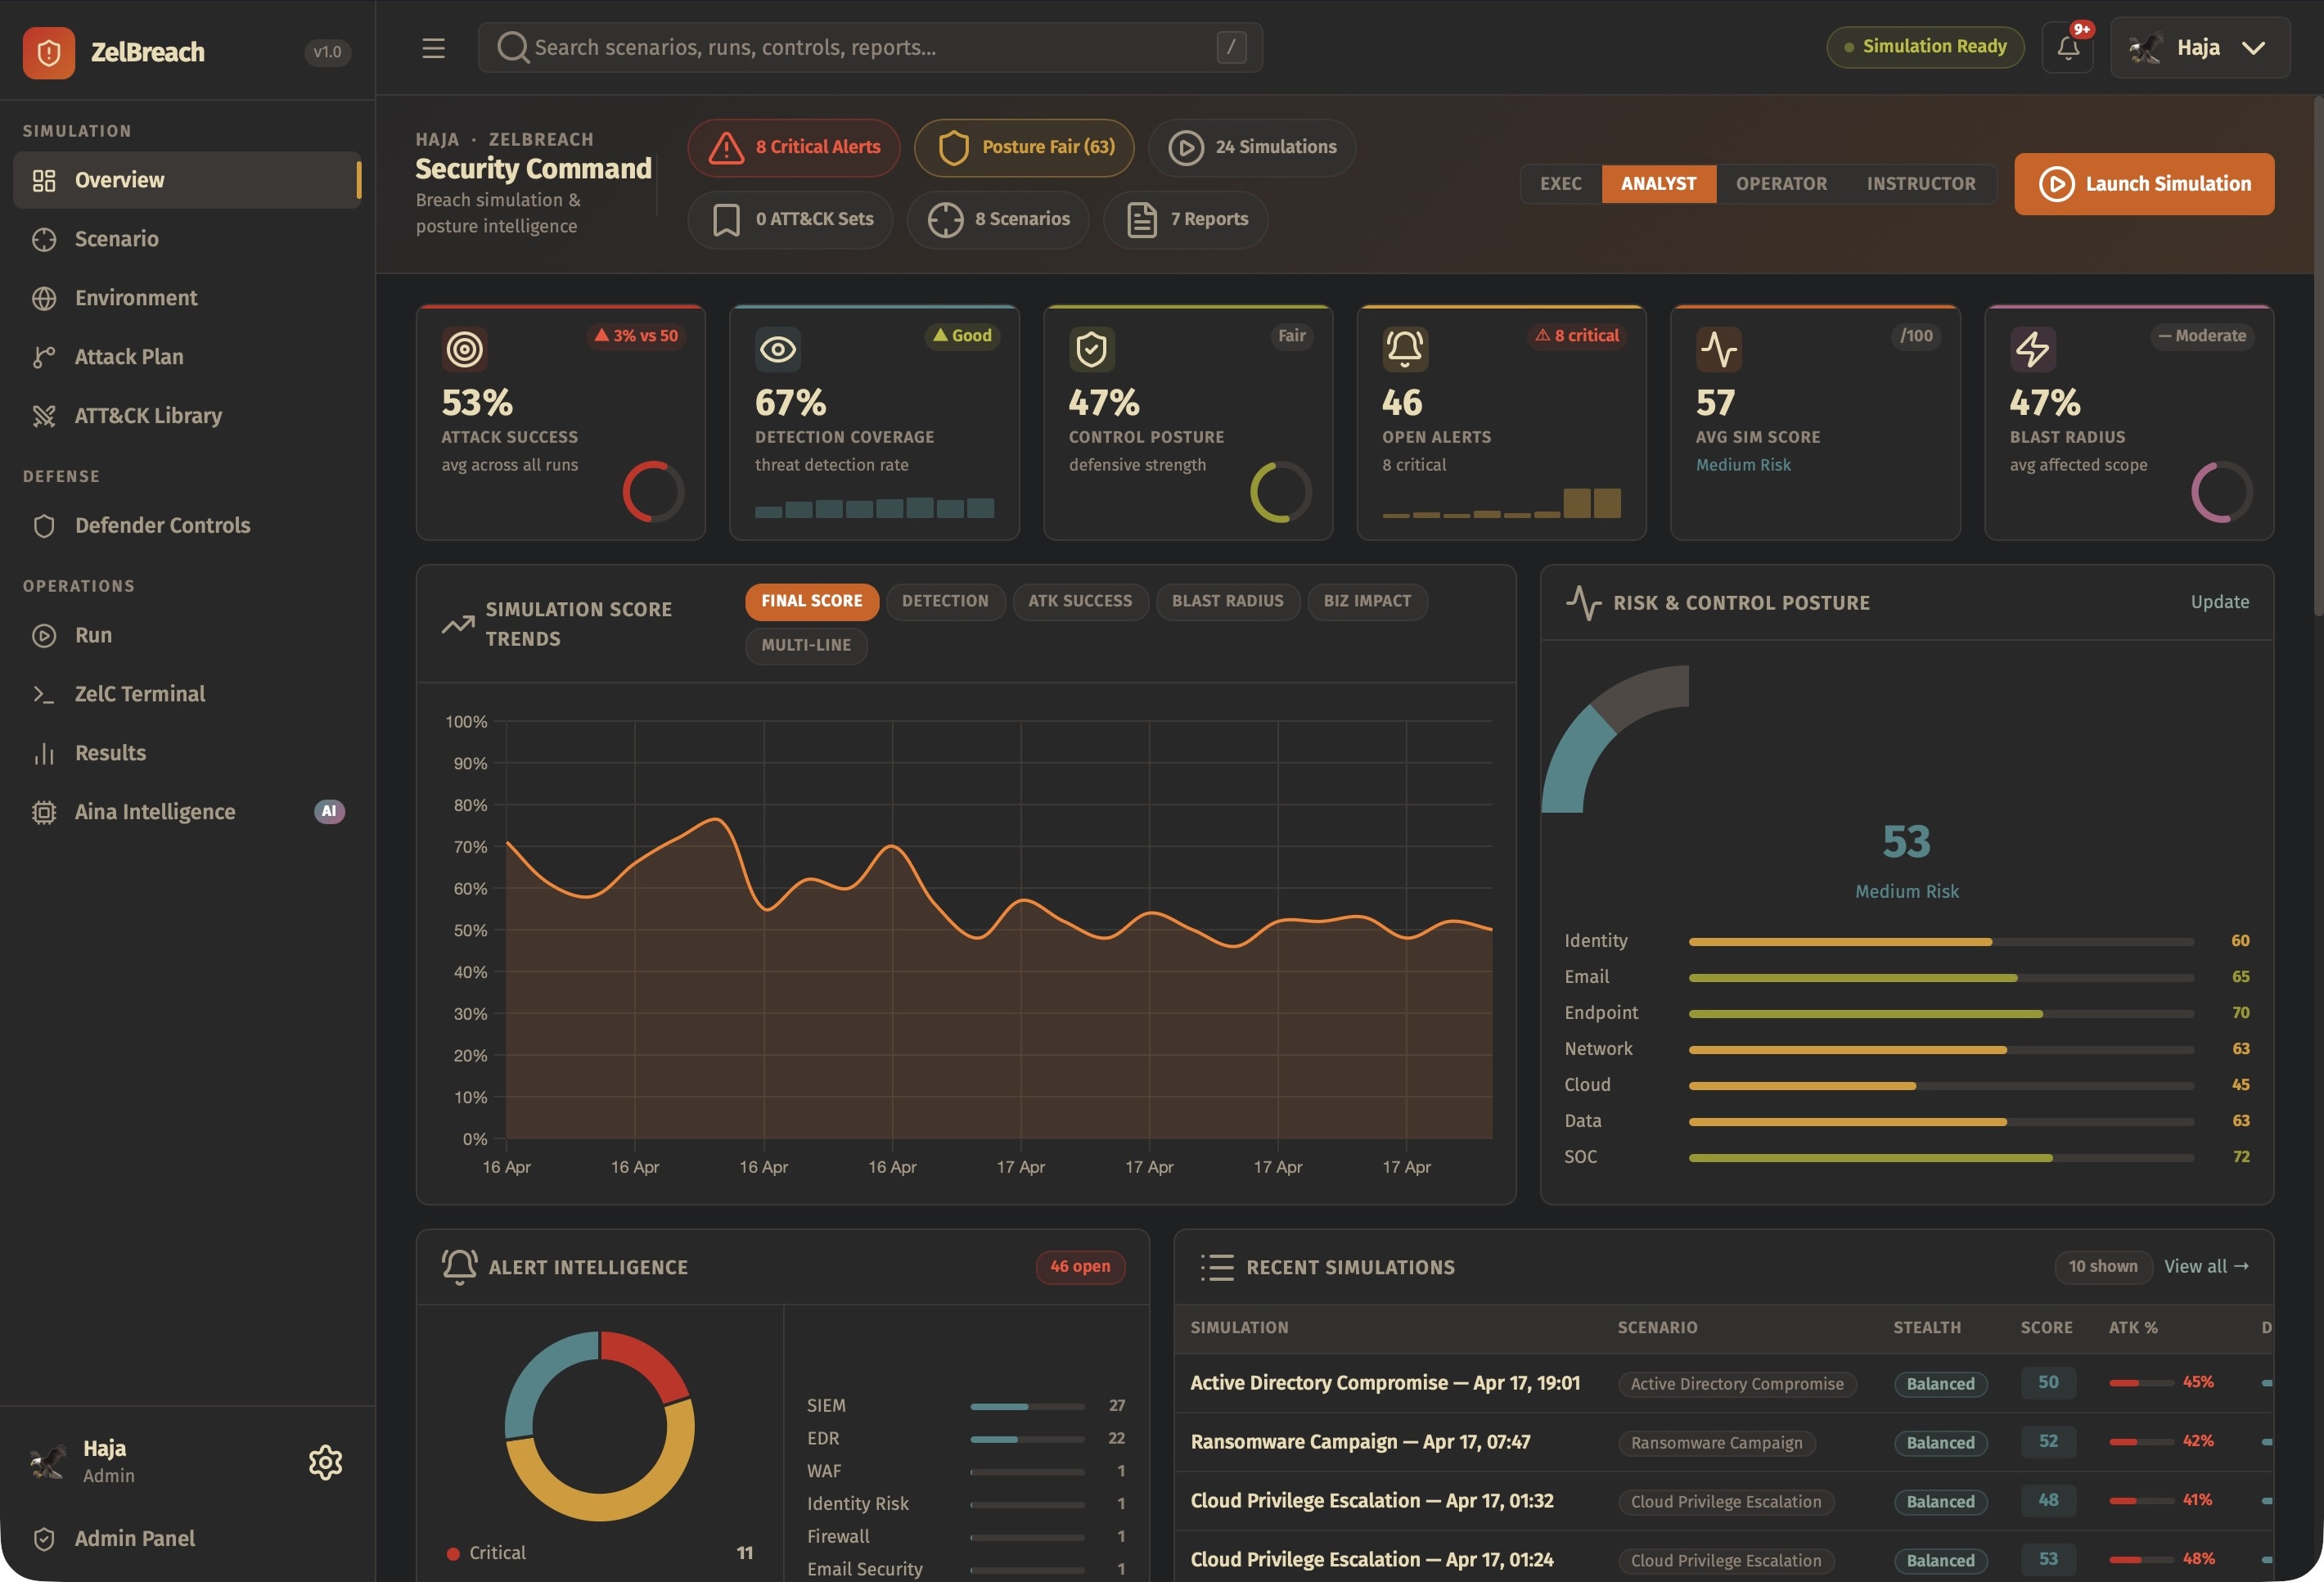
ZelBreach is built to connect technical reality and leadership clarity. It gives analysts a way to study techniques, paths, alerts, controls, and evidence while giving executives a way to understand posture, crown-jewel exposure, risk trend, and what to fix next.
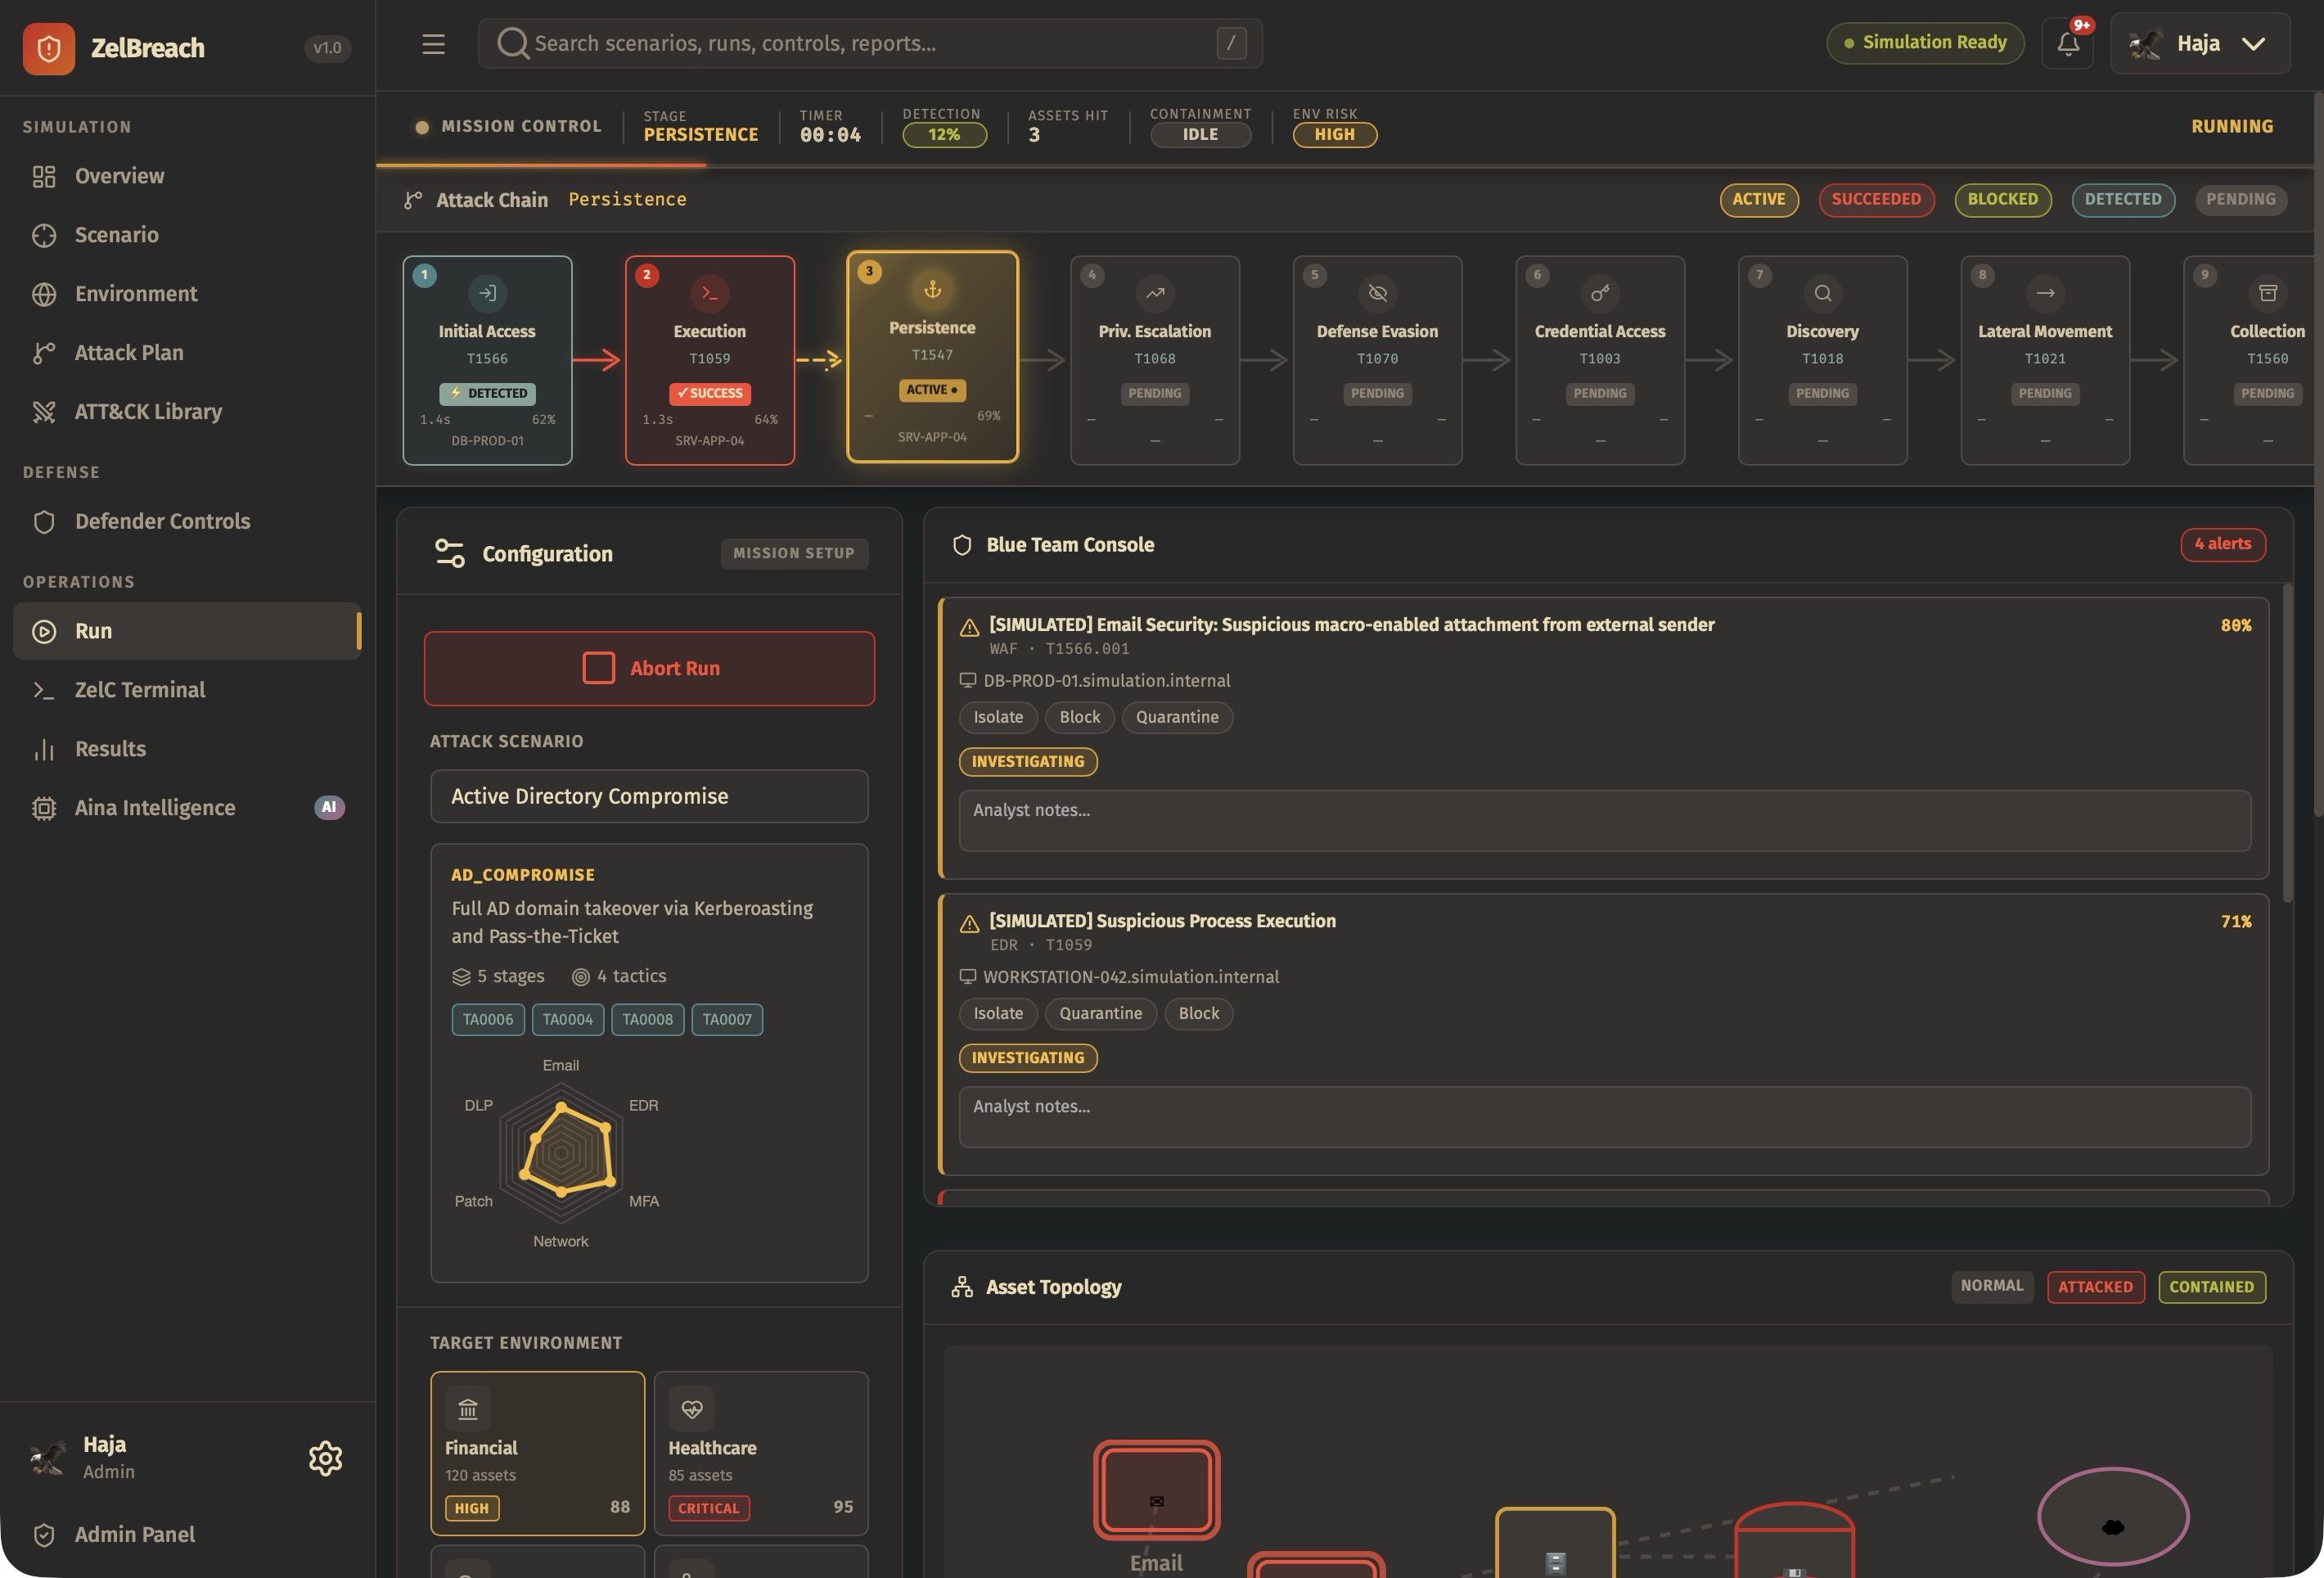
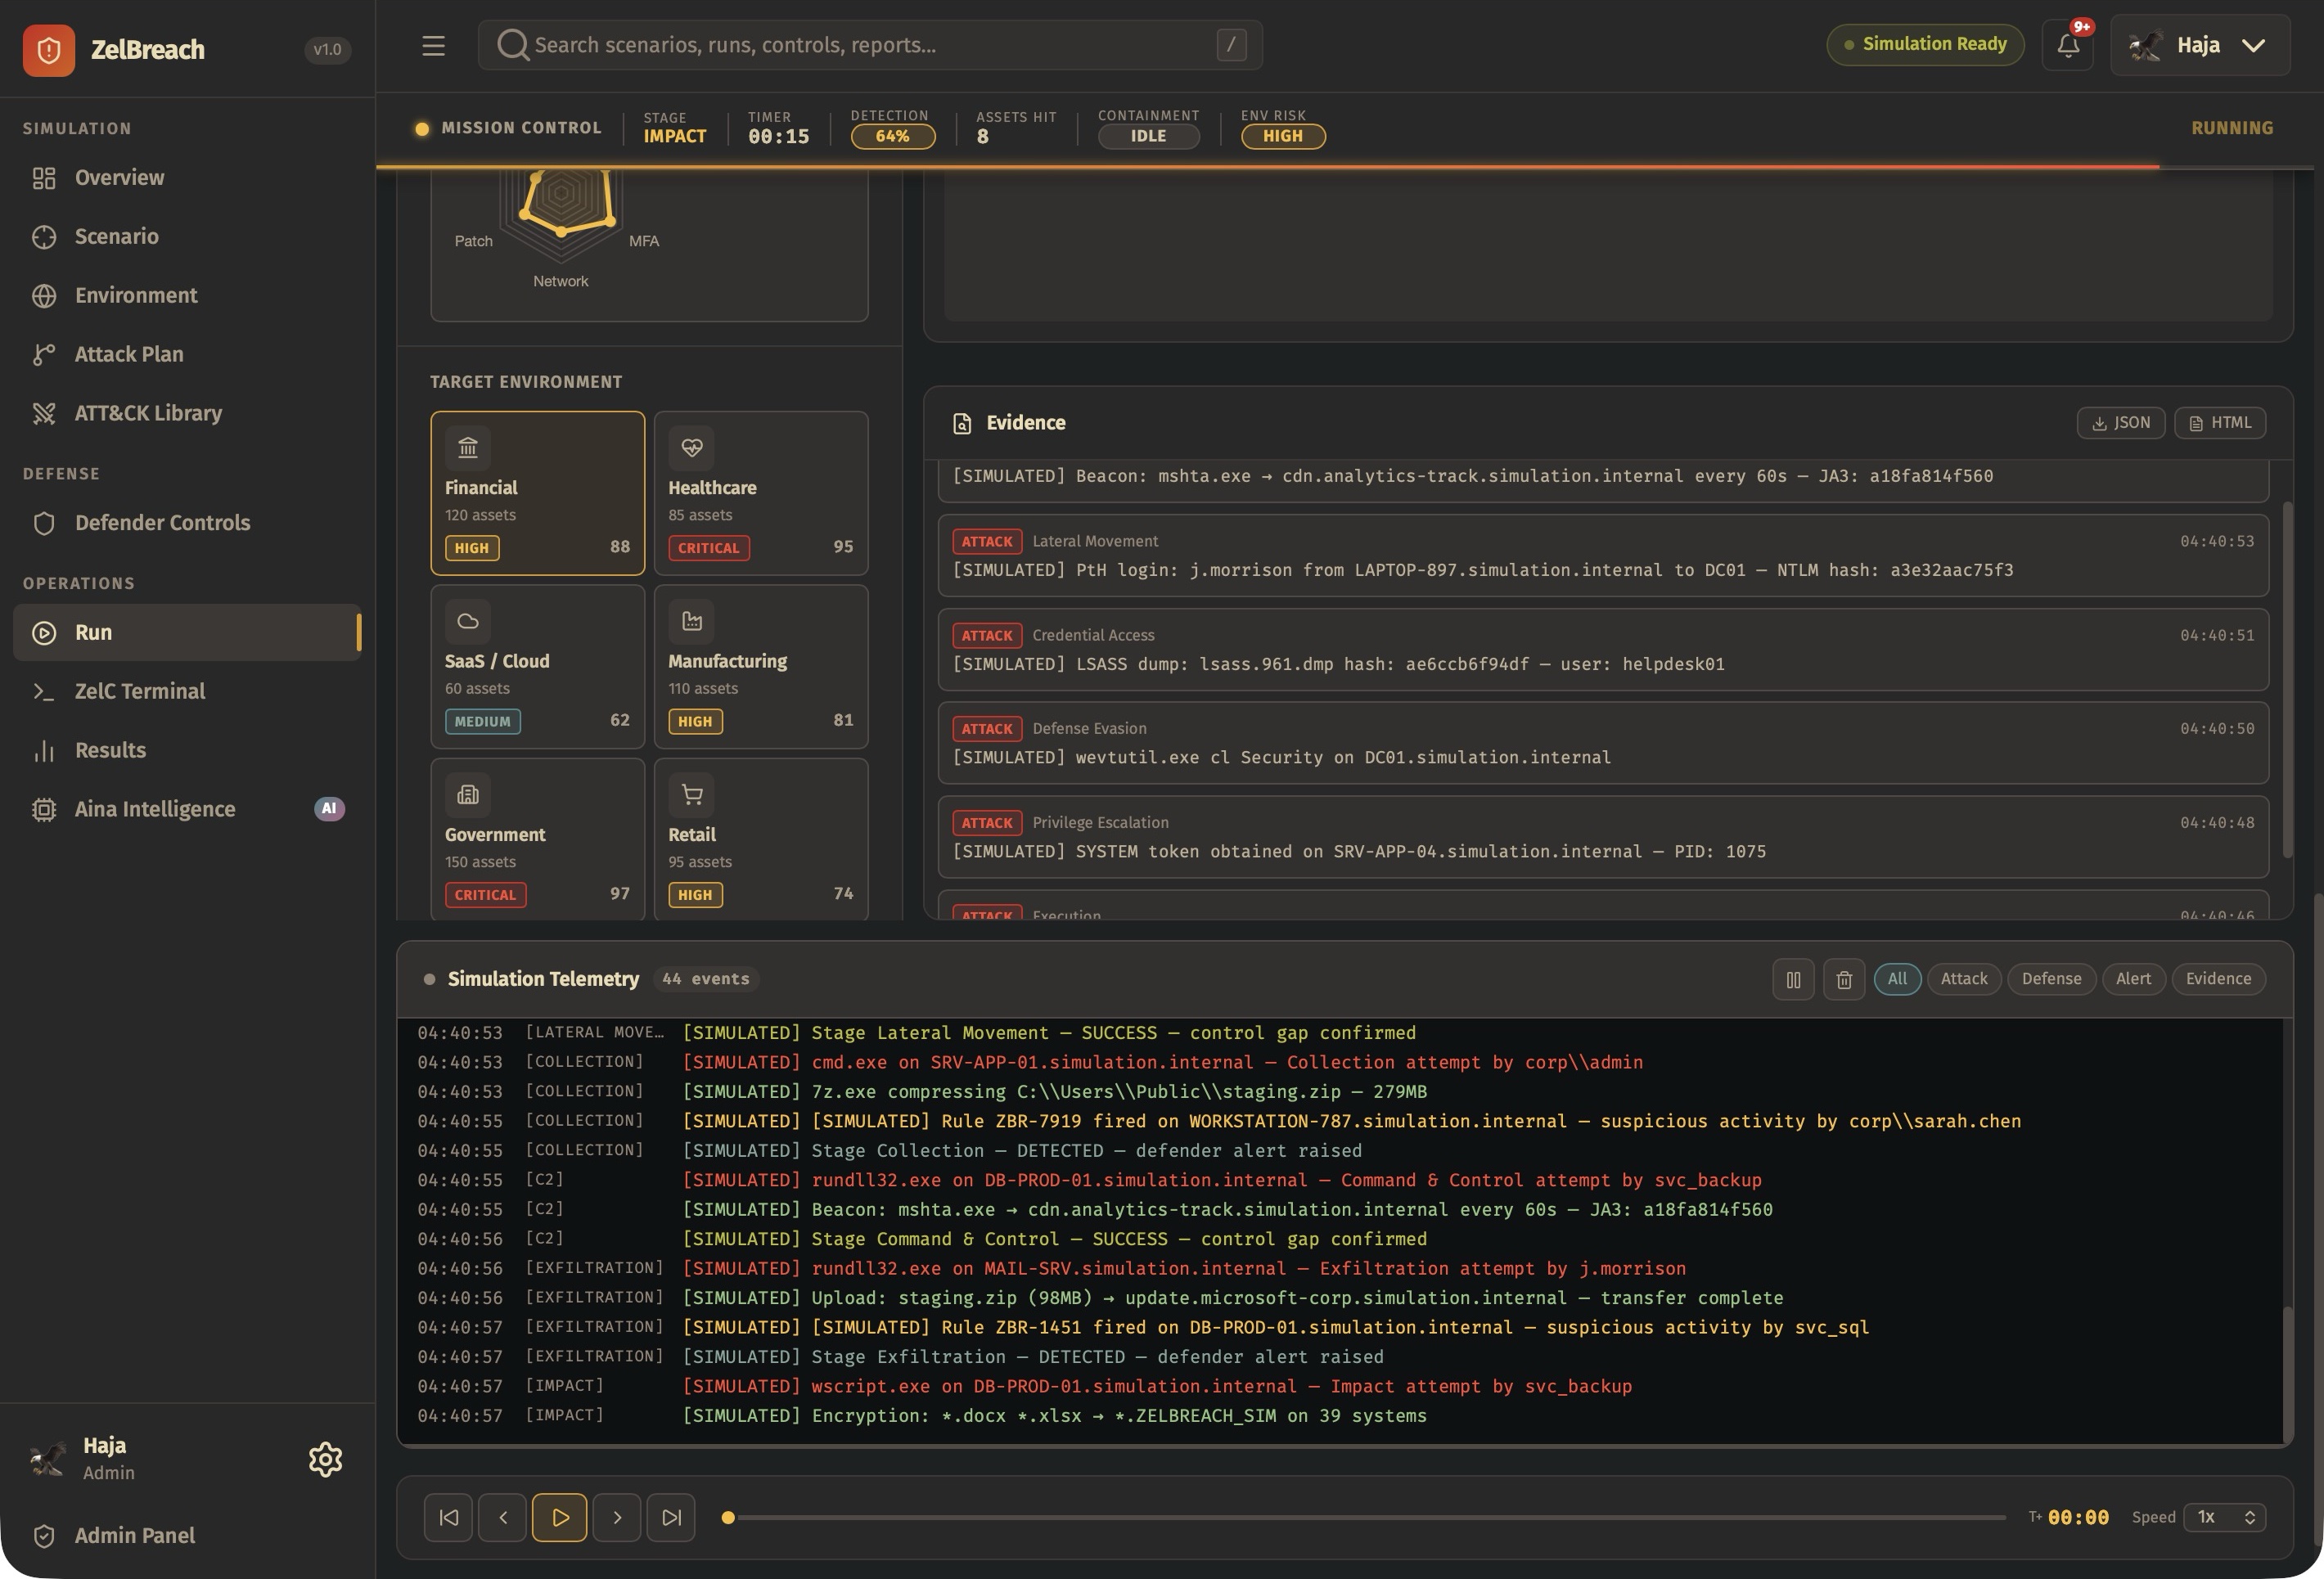
Model high-value cyber scenarios without touching real infrastructure. ZelBreach is built for simulation-only execution and decision support.
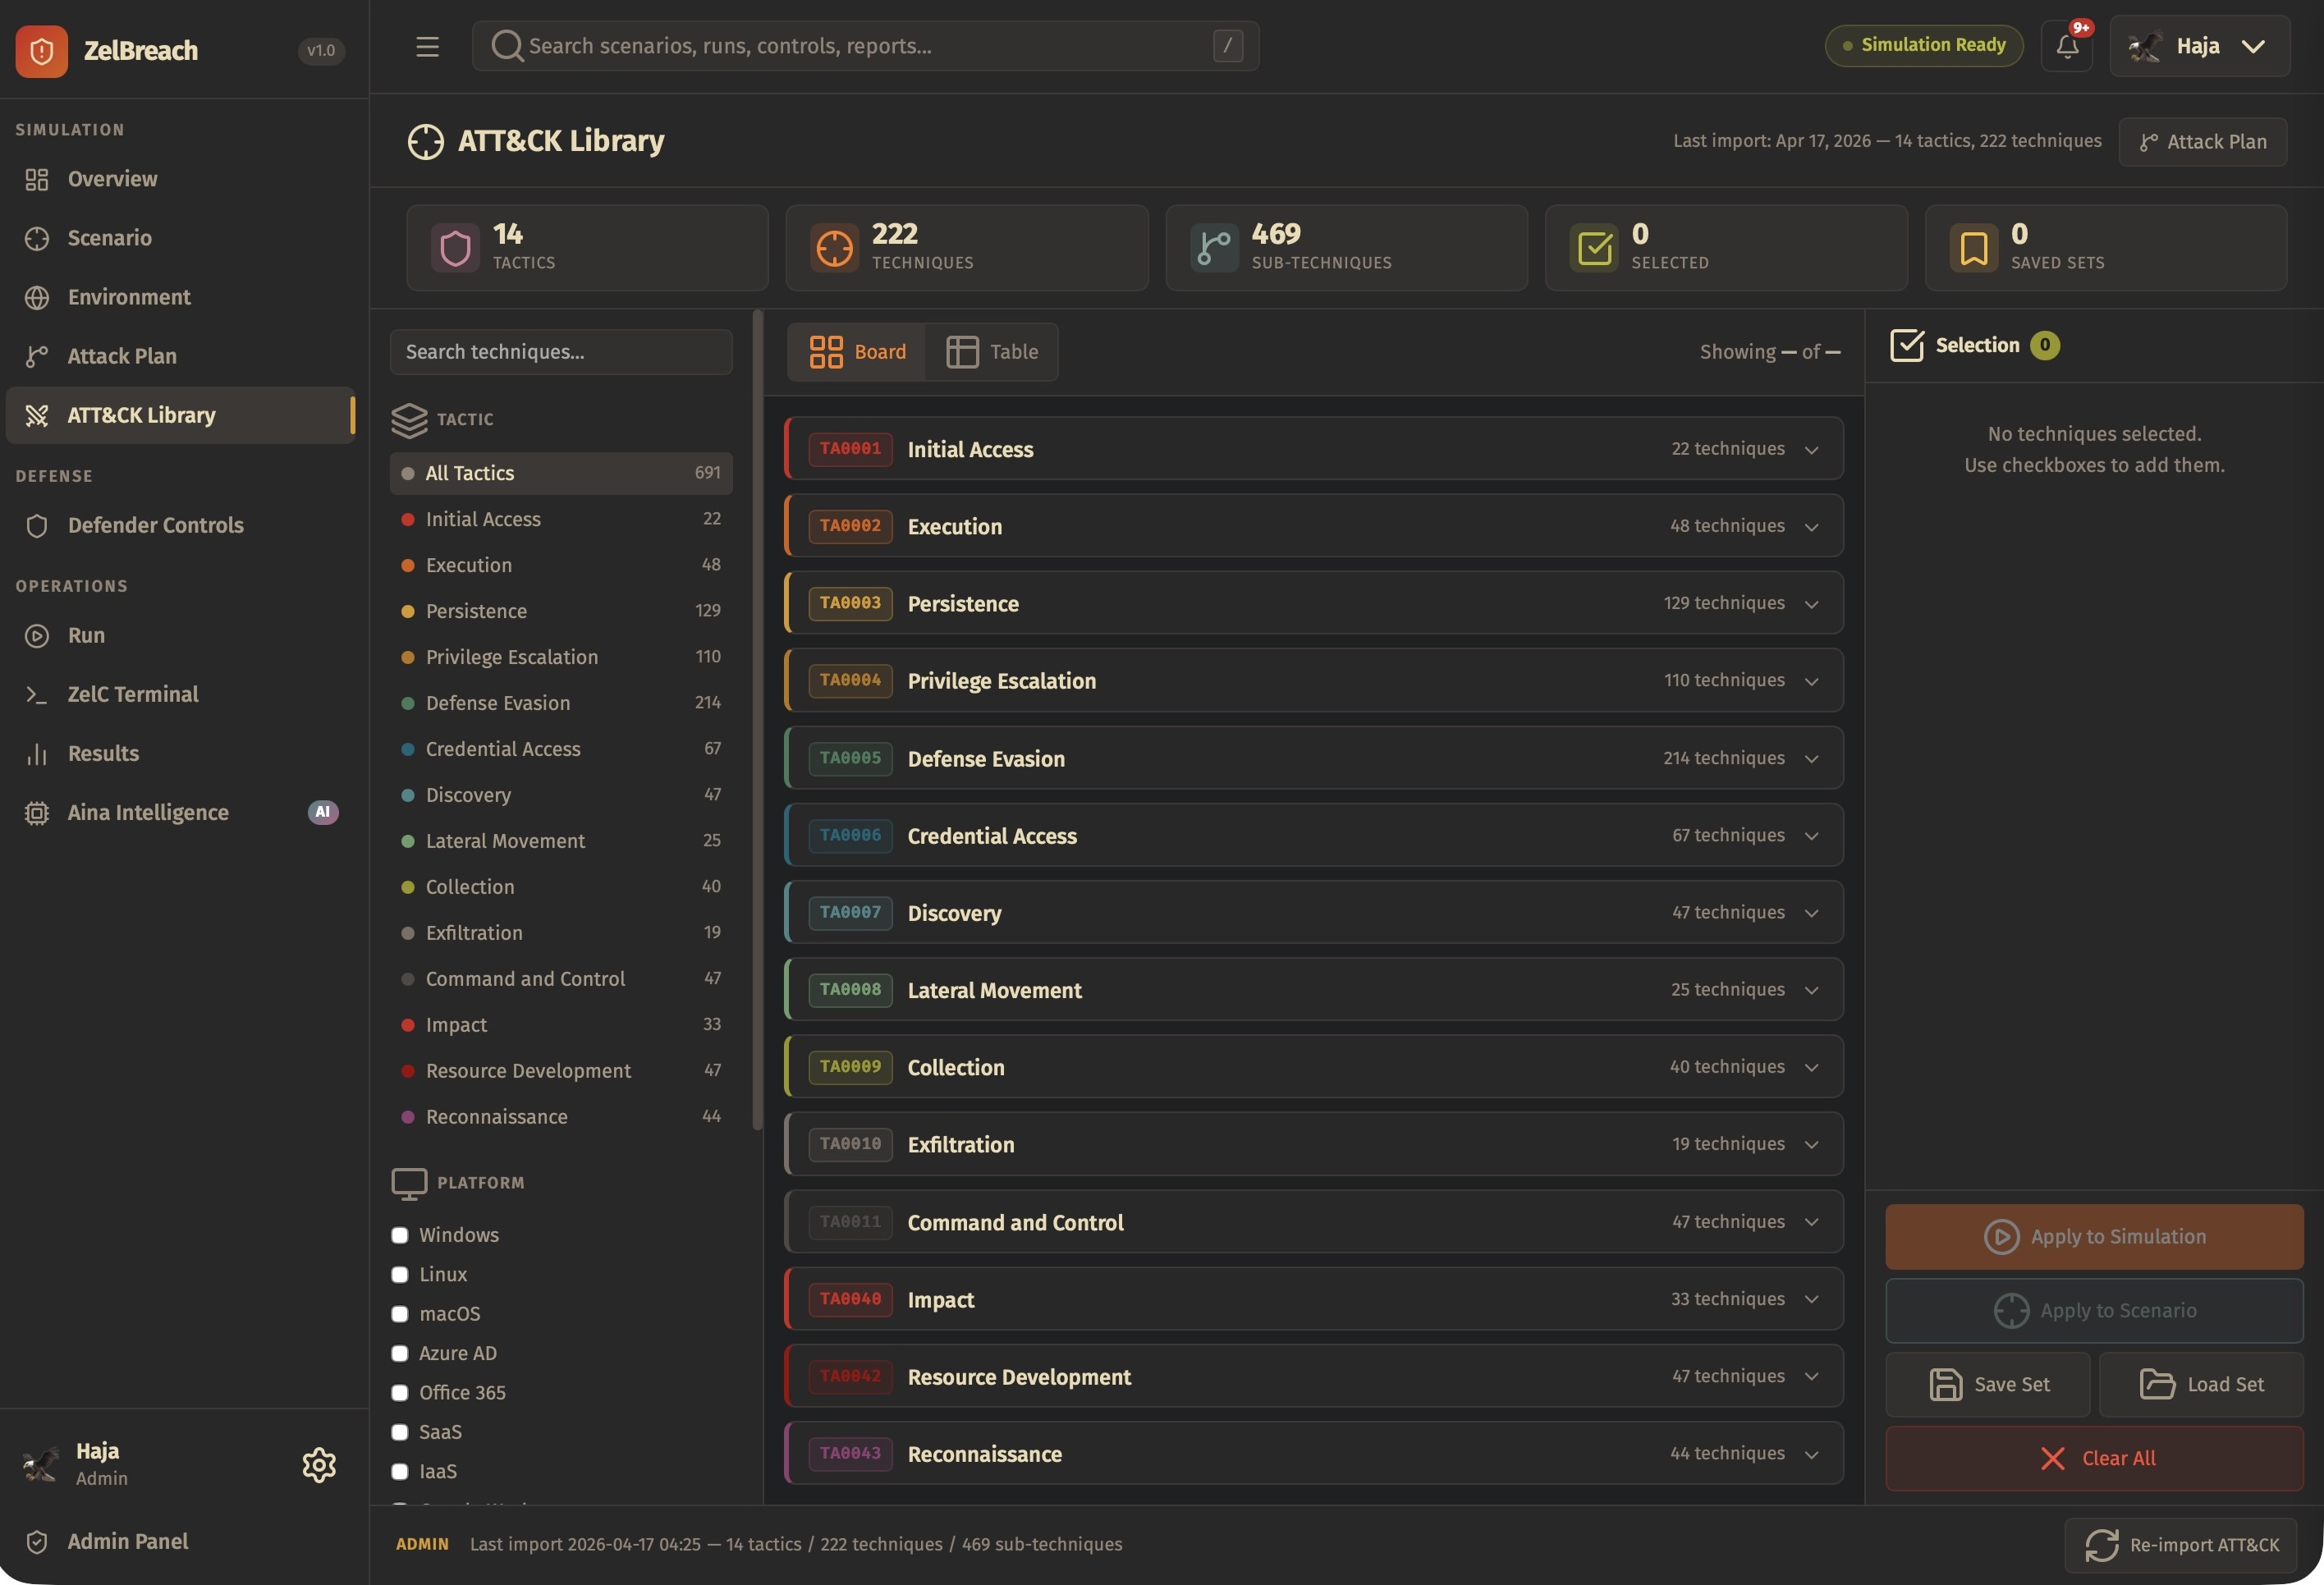
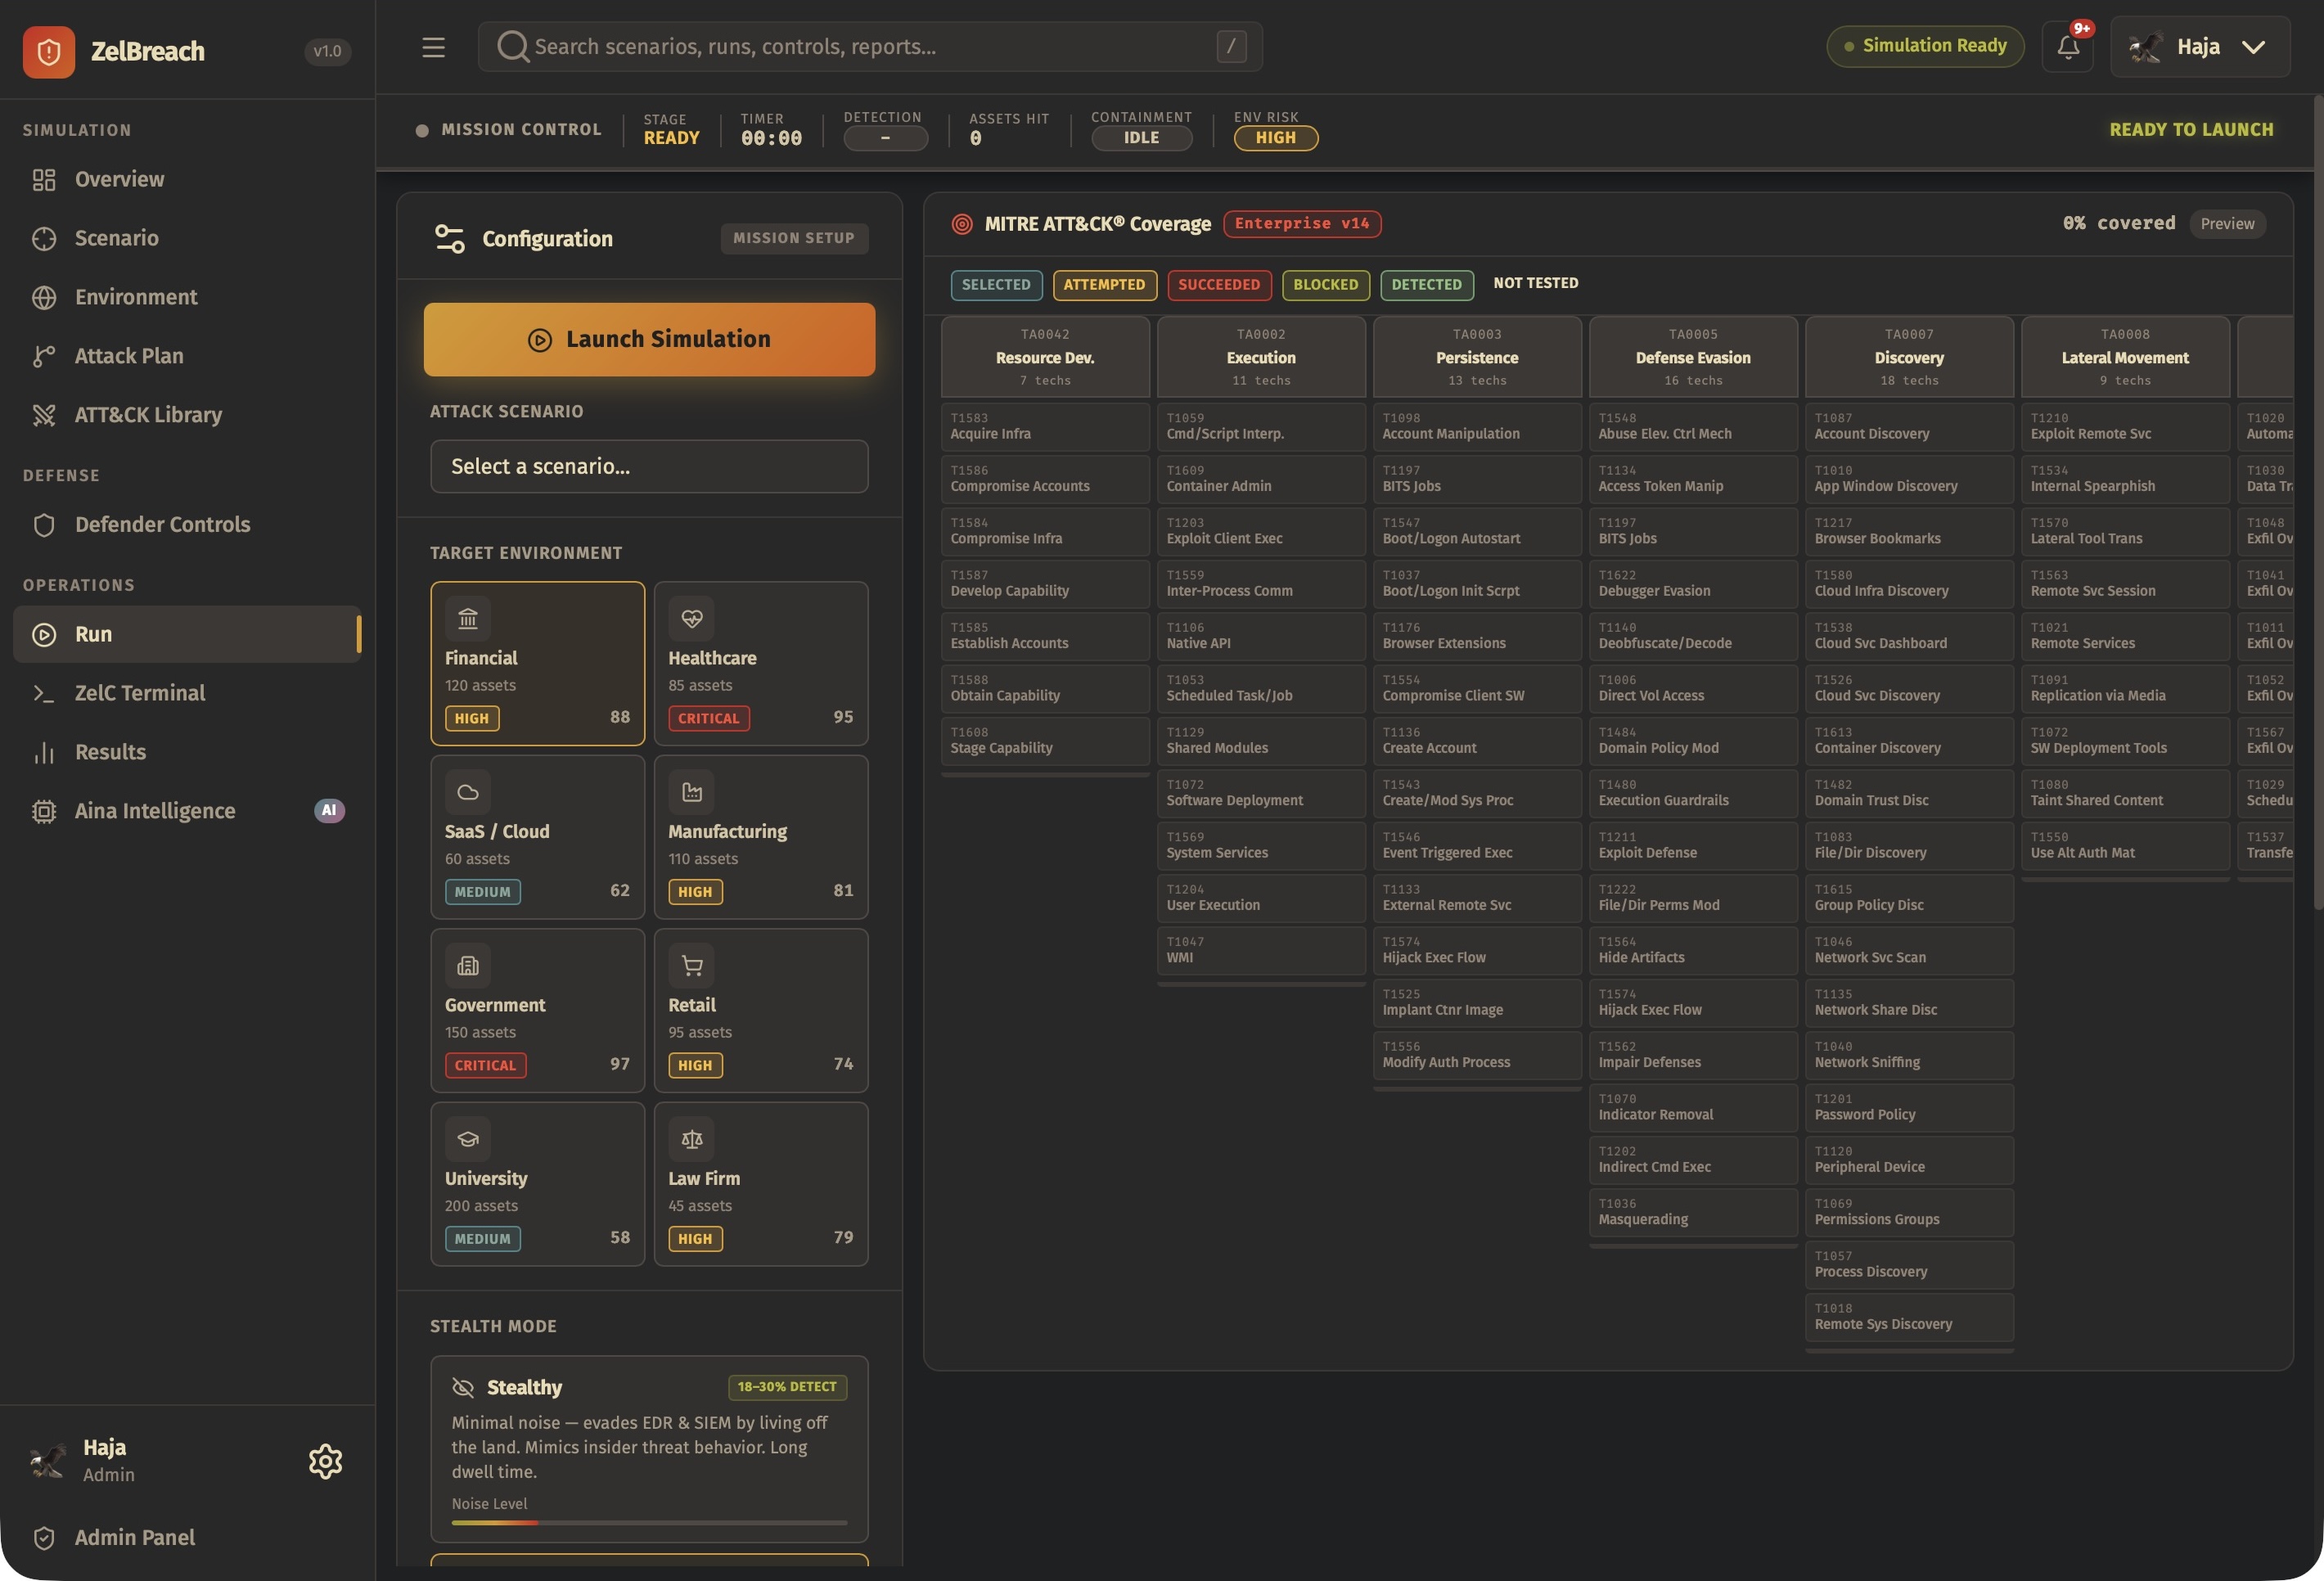
Browse tactics, techniques, and sub-techniques, save technique sets, and map ATT&CK coverage directly into scenarios and runs.
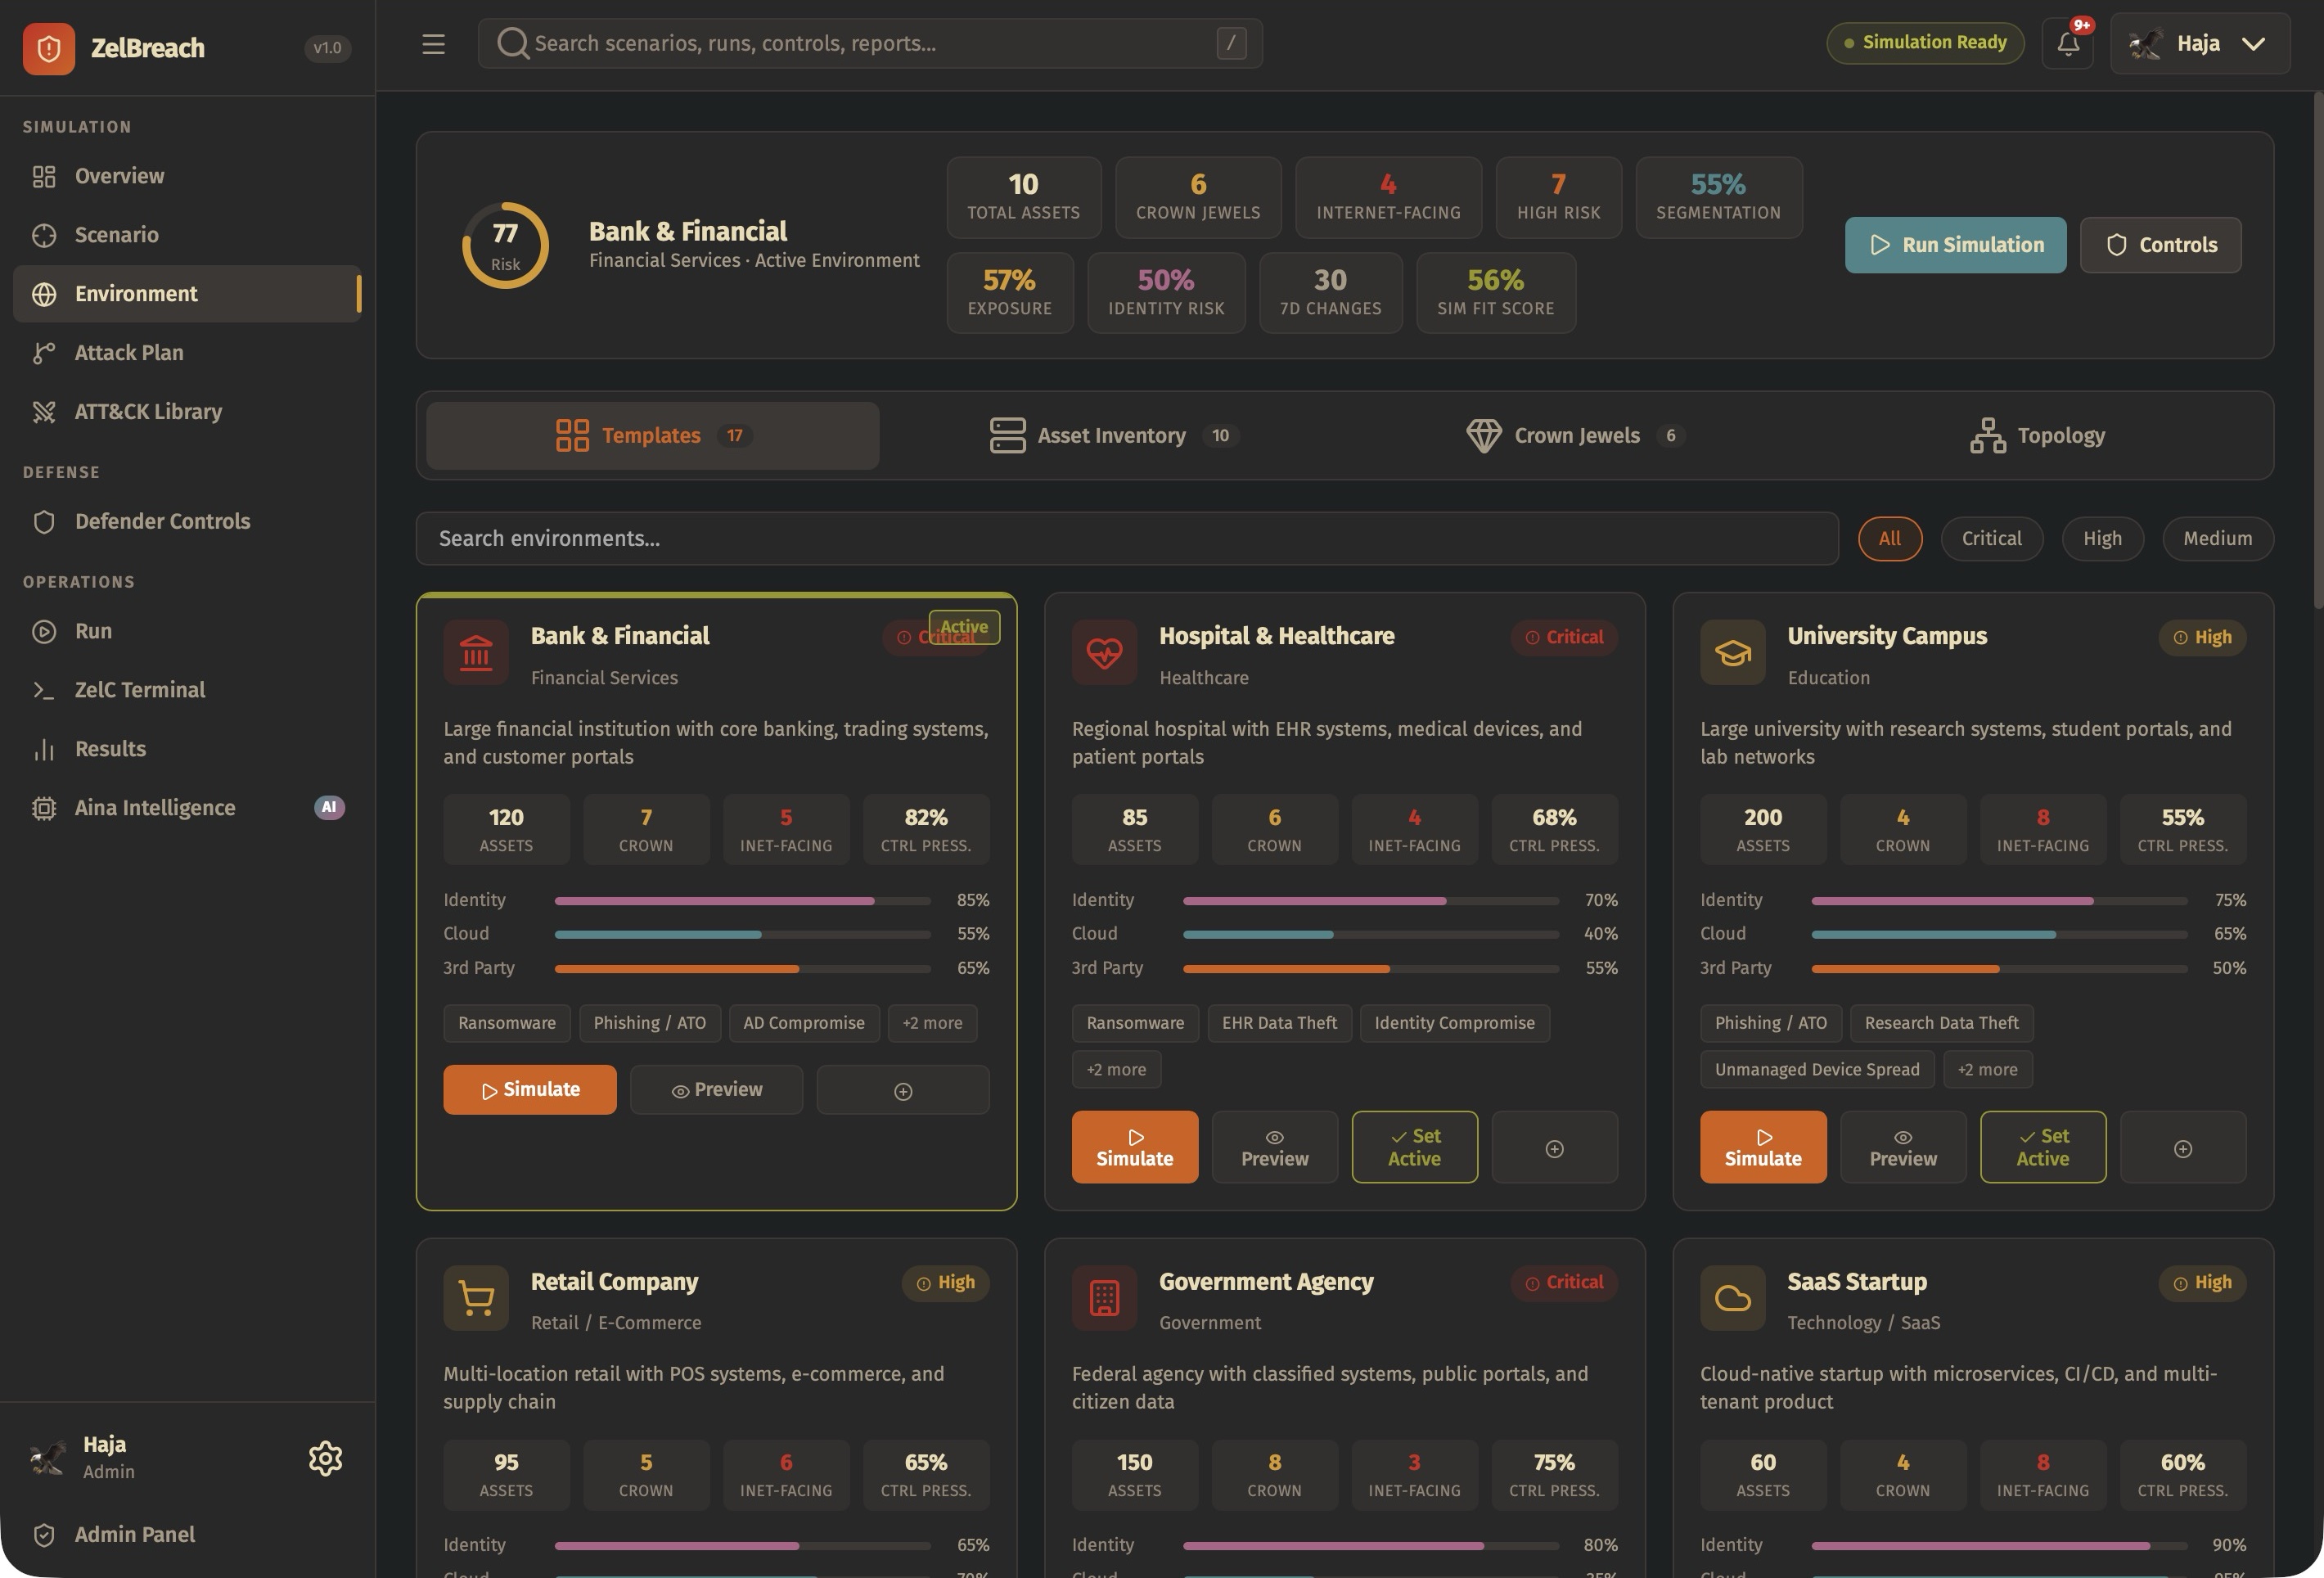
Build synthetic organizations with assets, crown jewels, trust zones, topology, exposure context, and environment-specific guidance.
Tune defender controls such as MFA, EDR, segmentation, WAF, DLP, backups, SIEM, and cloud guardrails to see how results change.
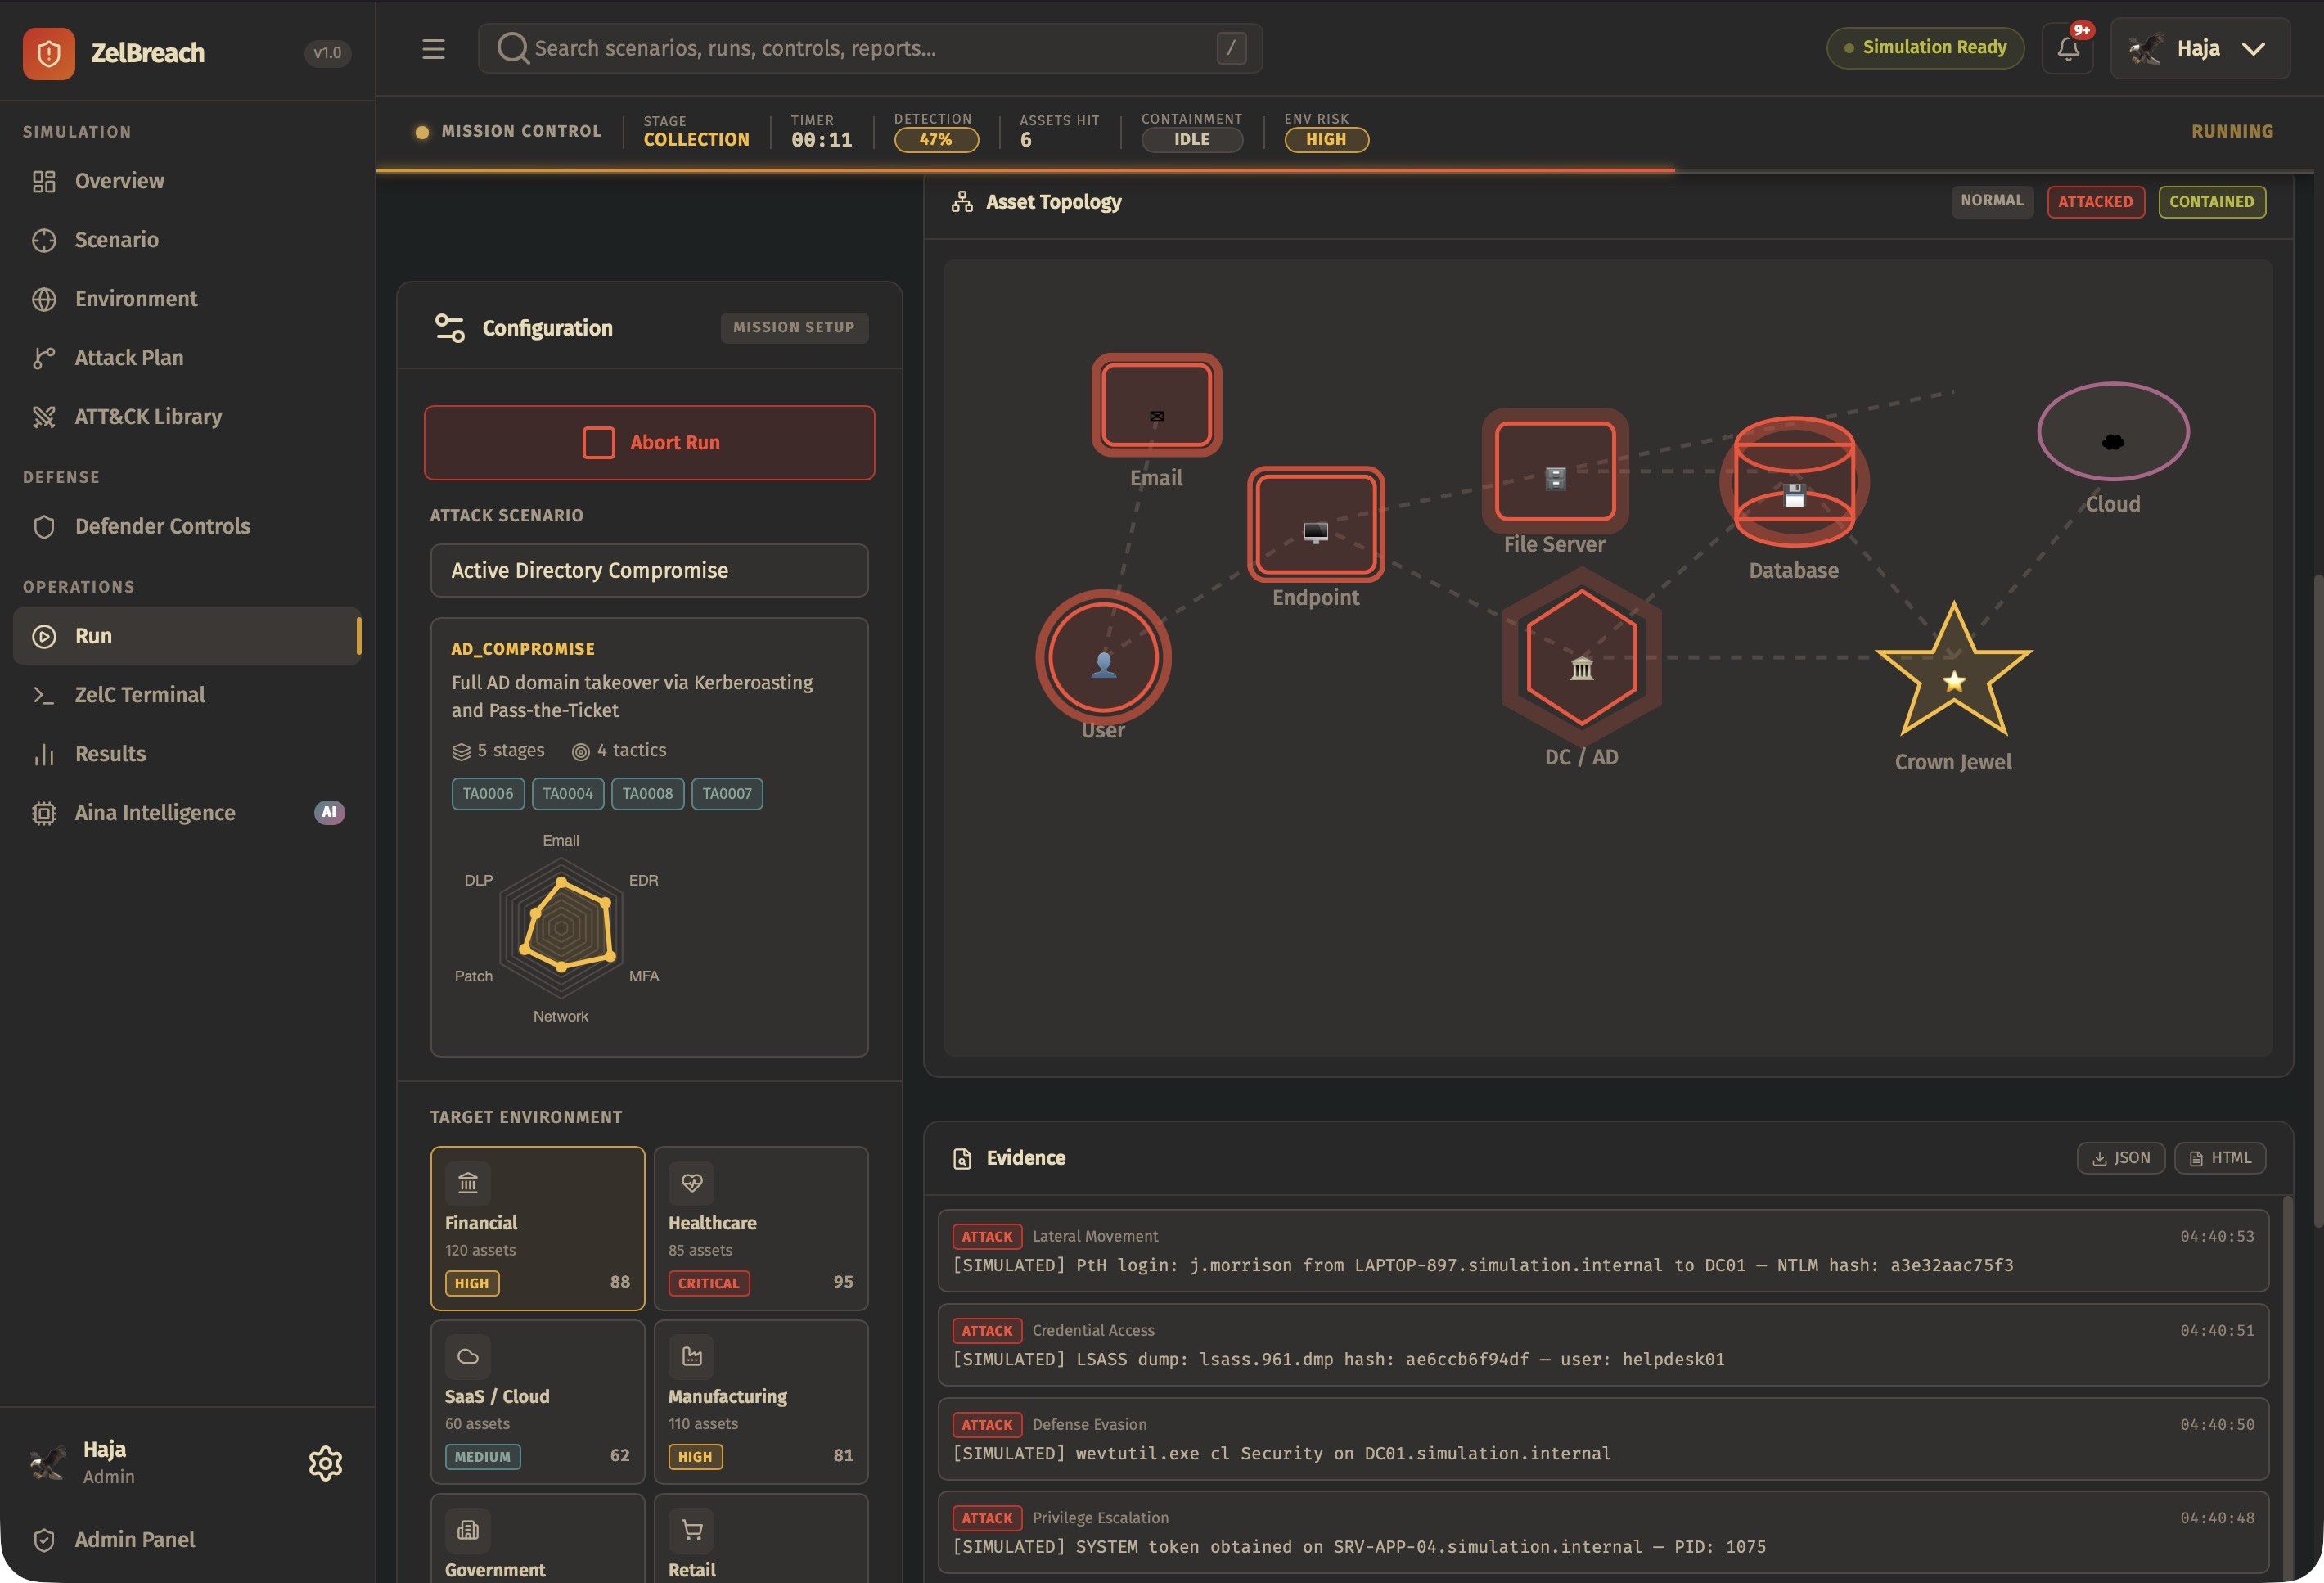
Analysts get alerts, evidence, coverage, and traces. Leaders get posture, blast radius, business impact, and next actions.
Use Aina Intelligence for summaries and recommendations, and ZelC Terminal for safe simulation playbooks and execution previews.
UNDER THE HOOD
Architecture, integrations, security controls, and operational details for ZelBreach.
INSIDE ZELBREACH
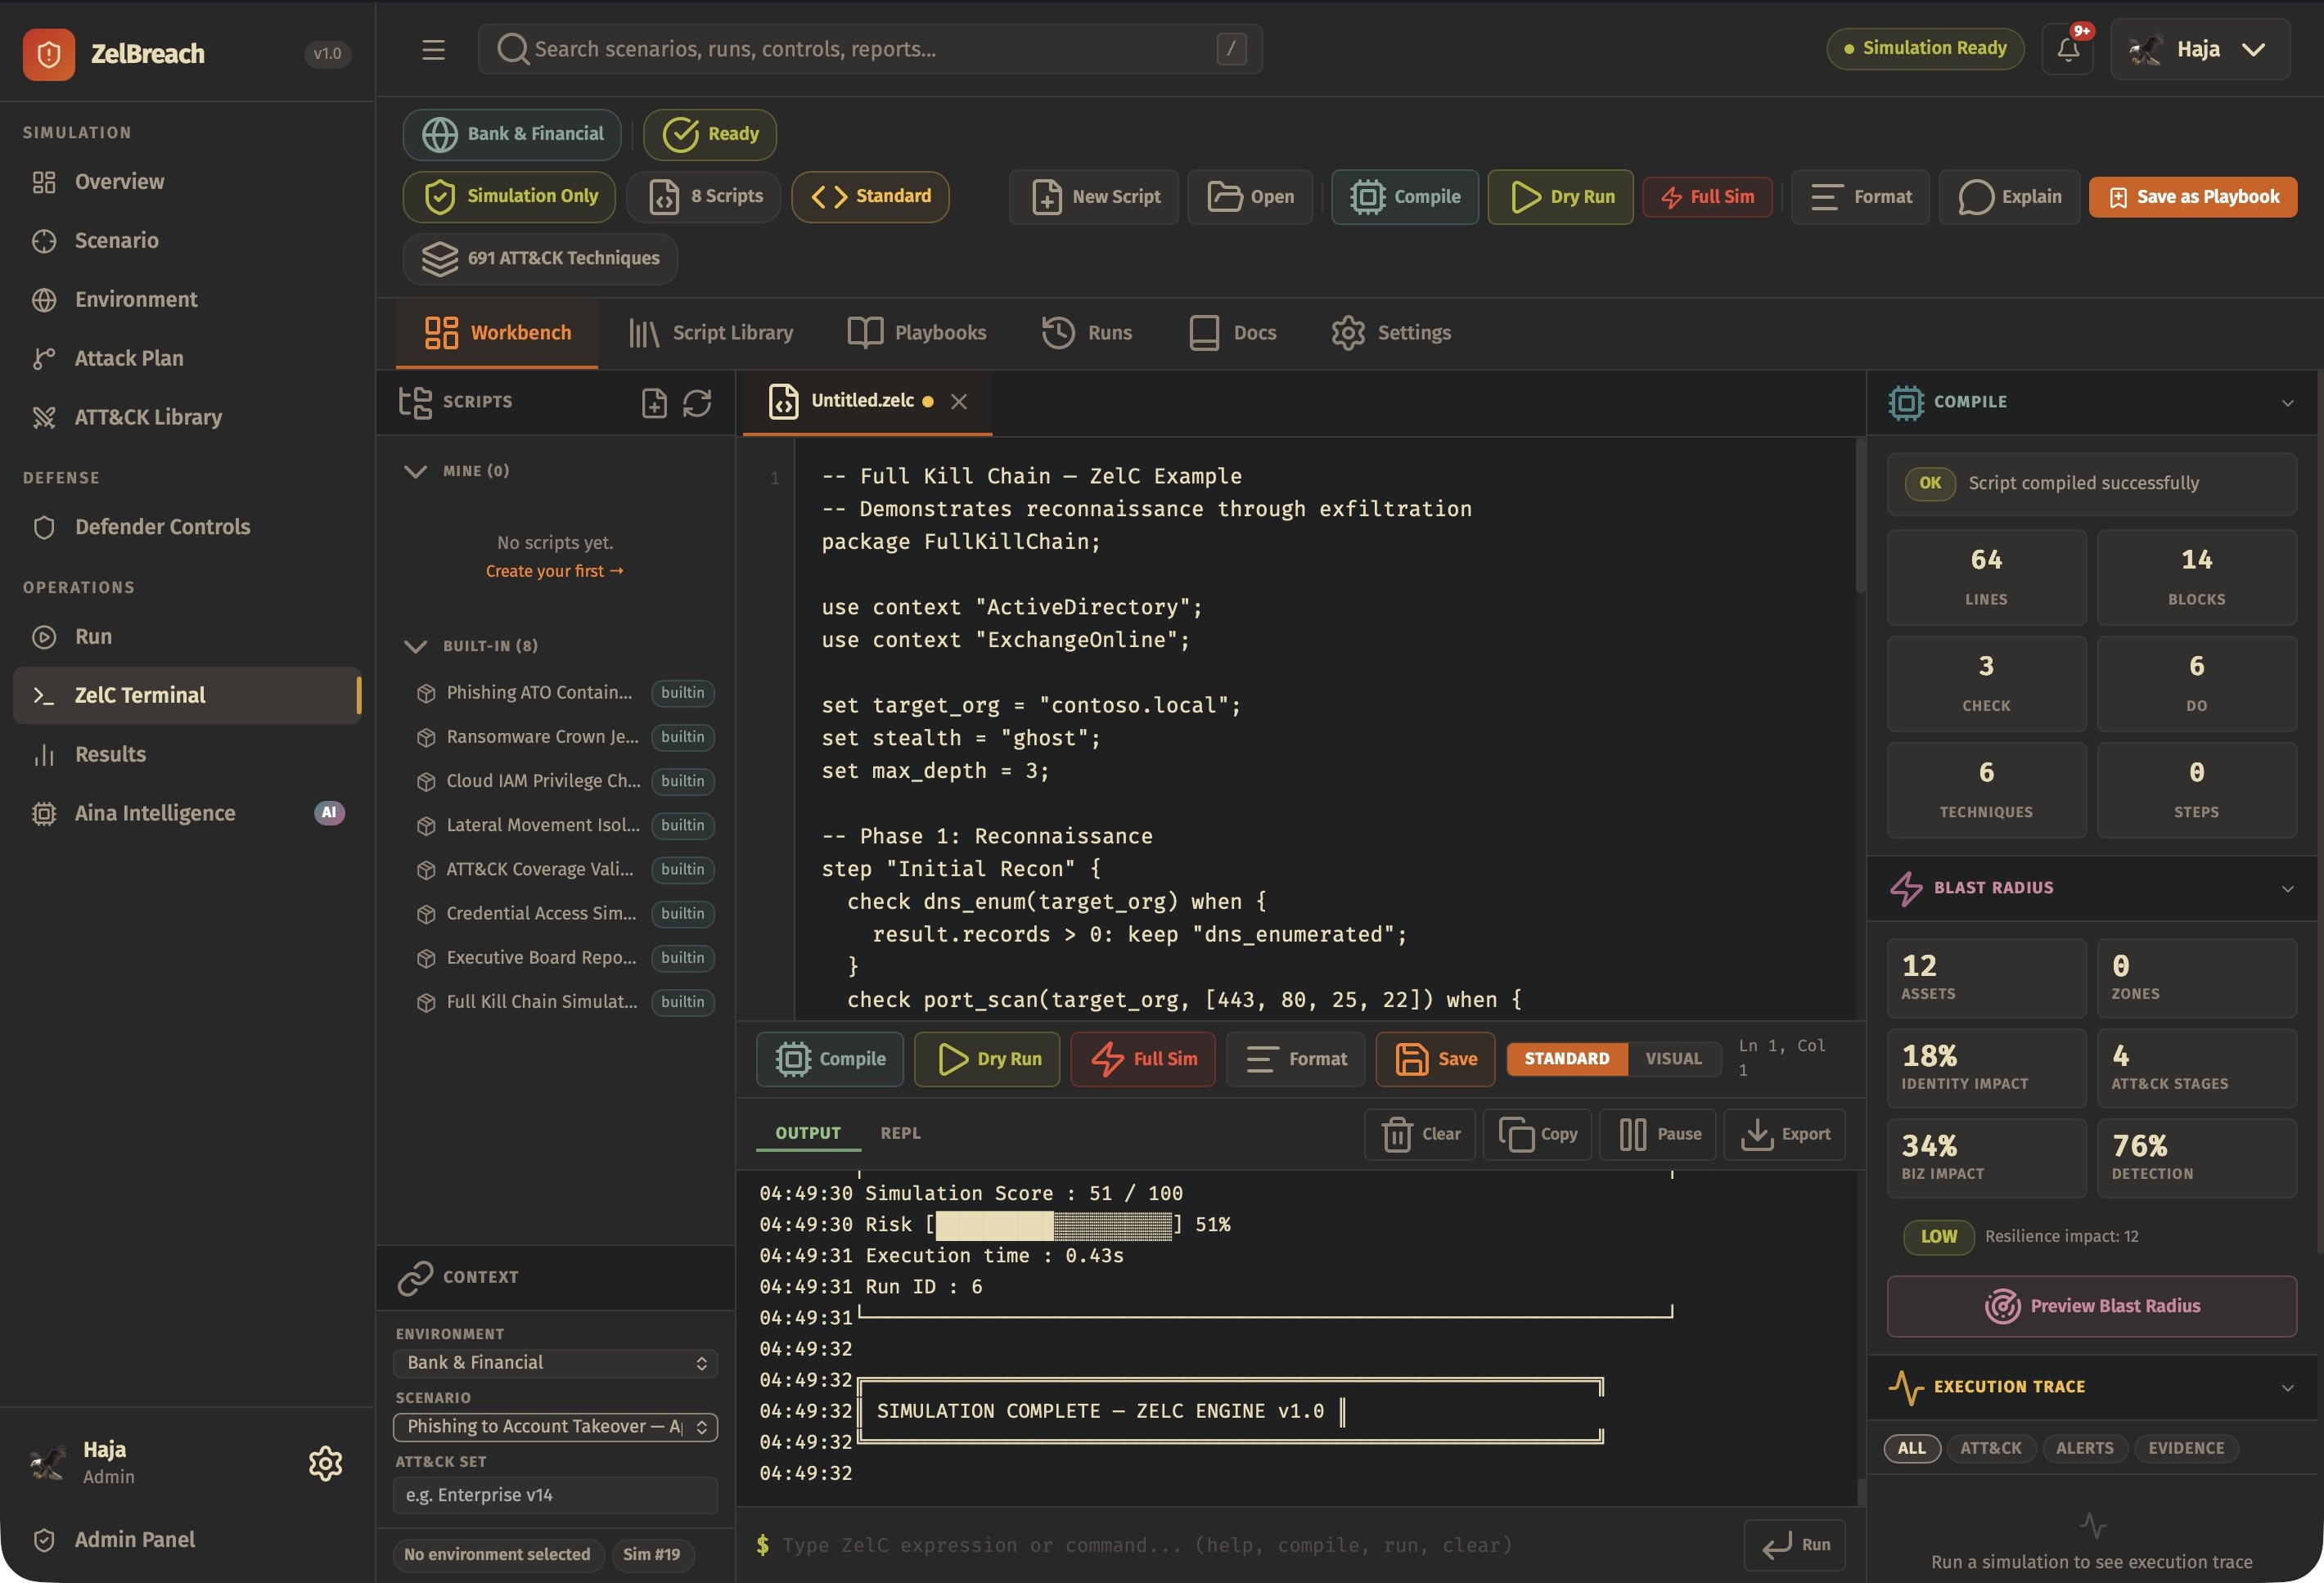
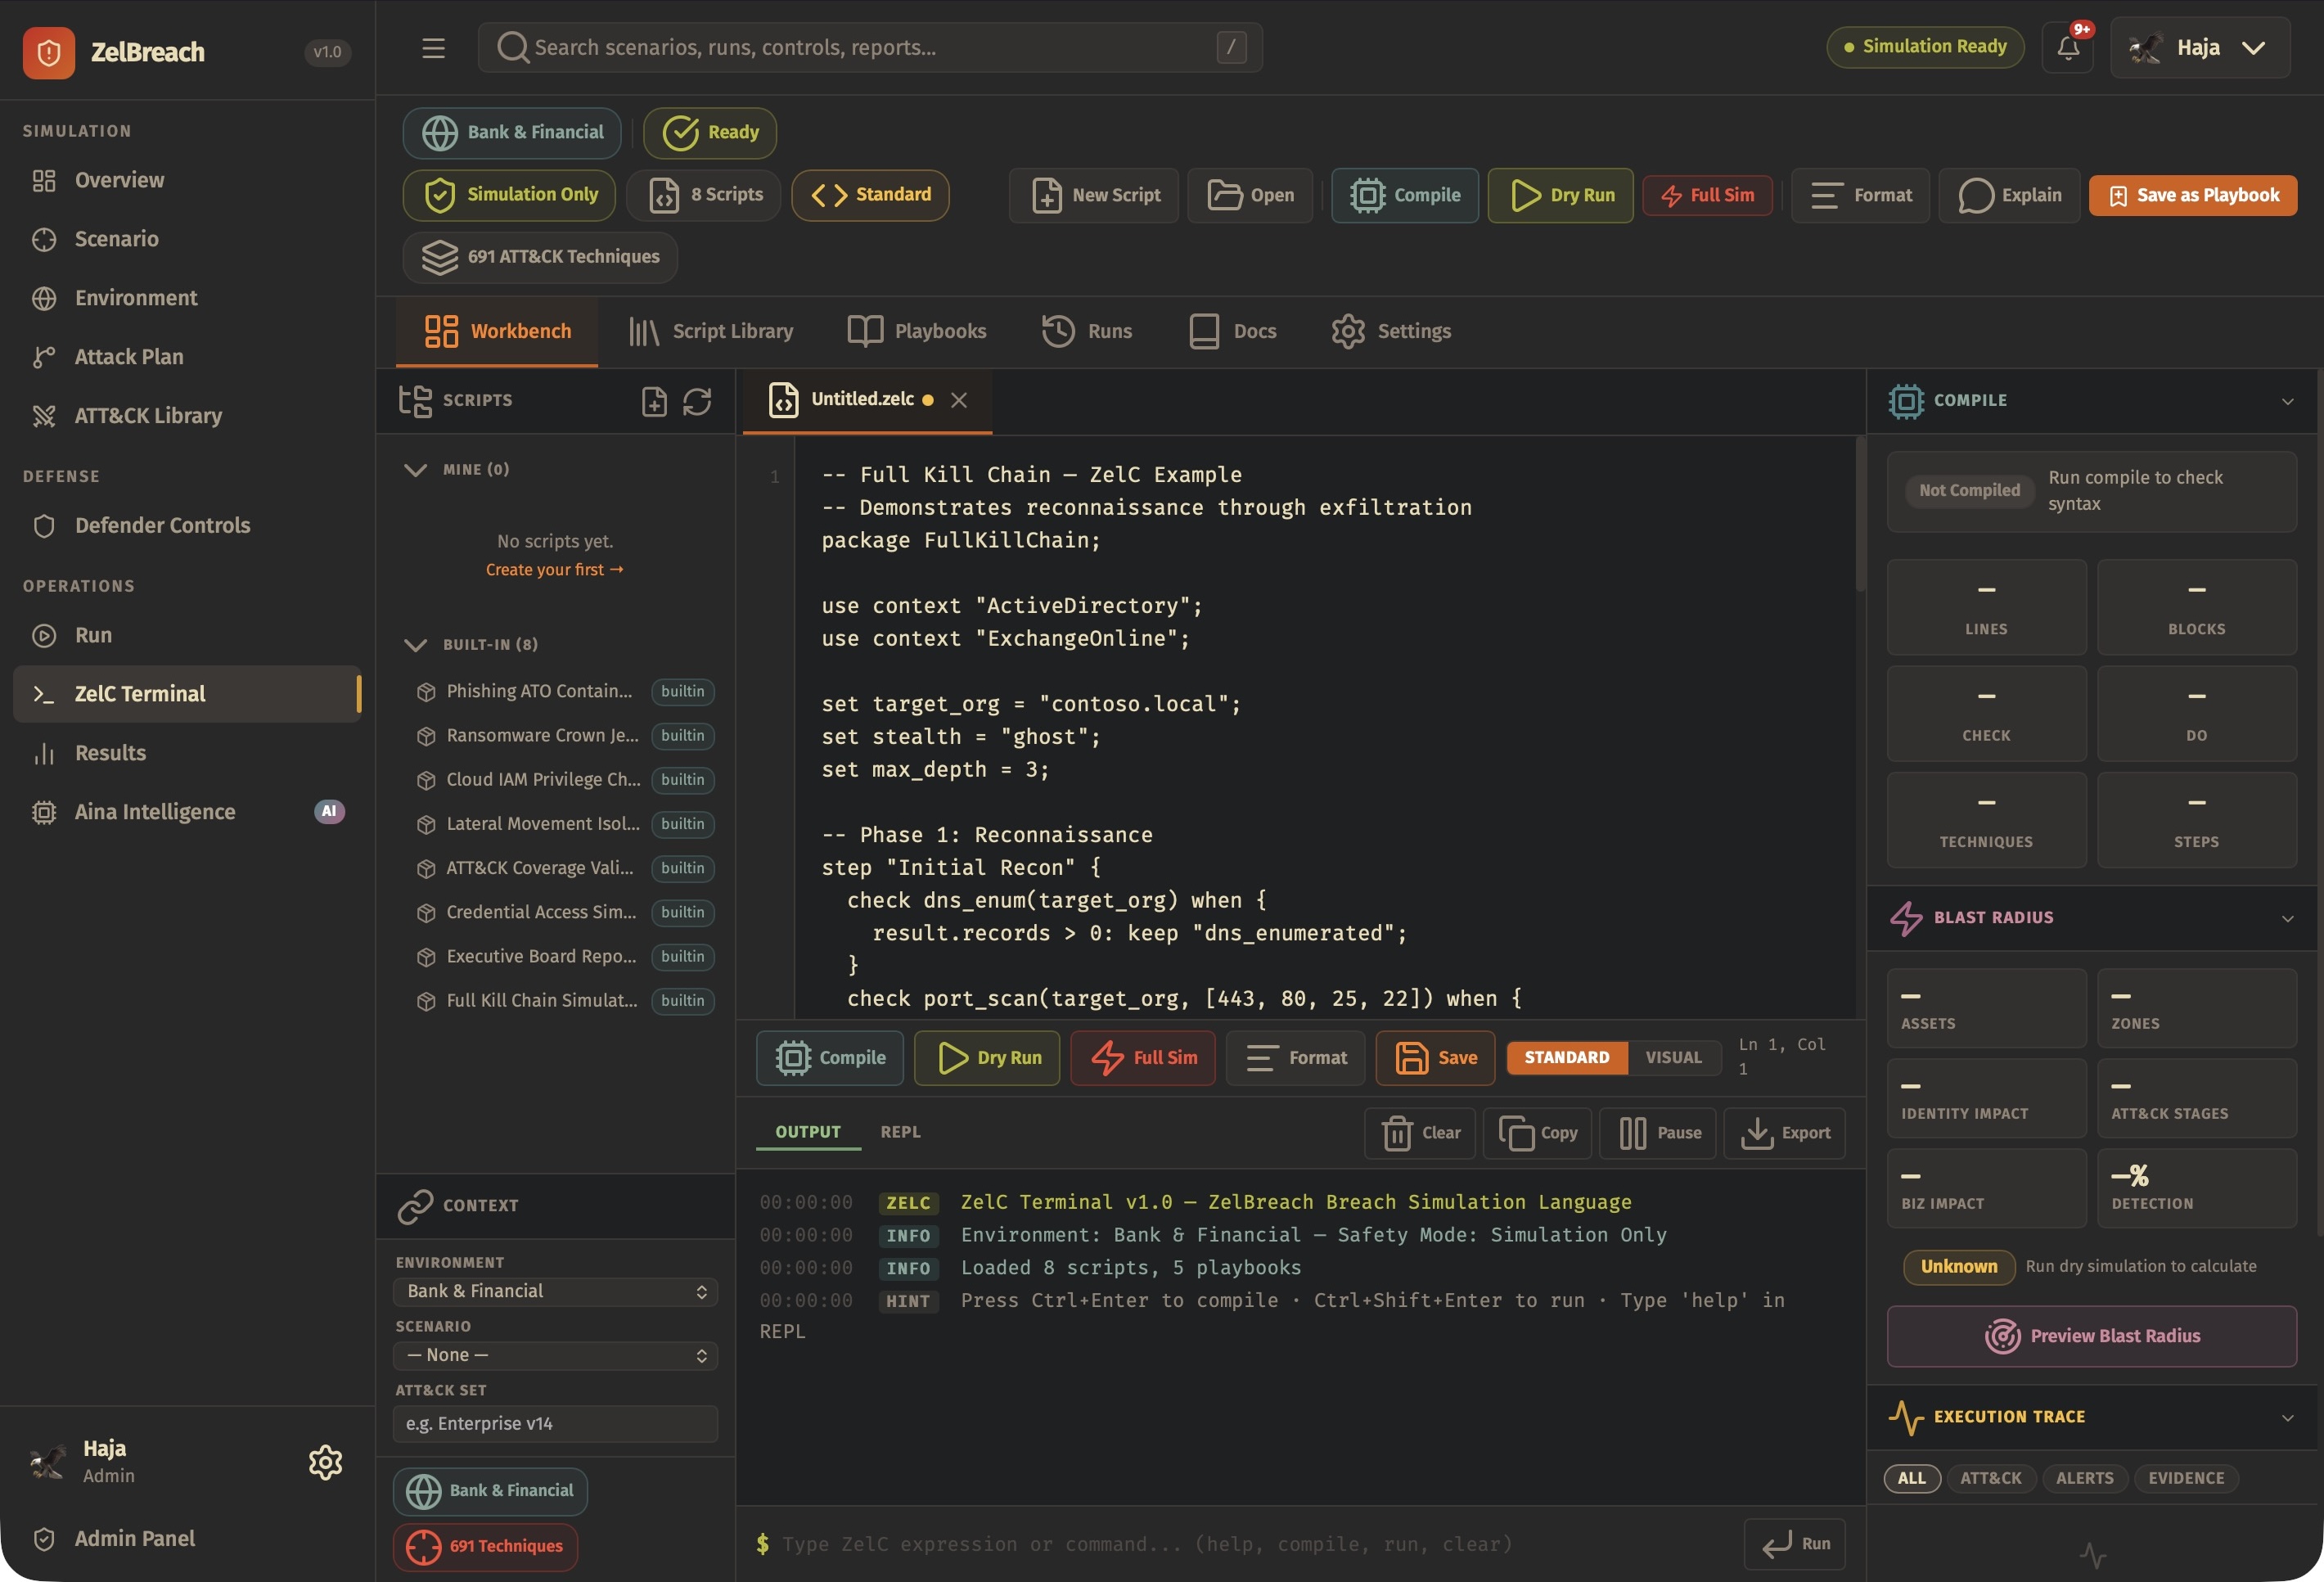
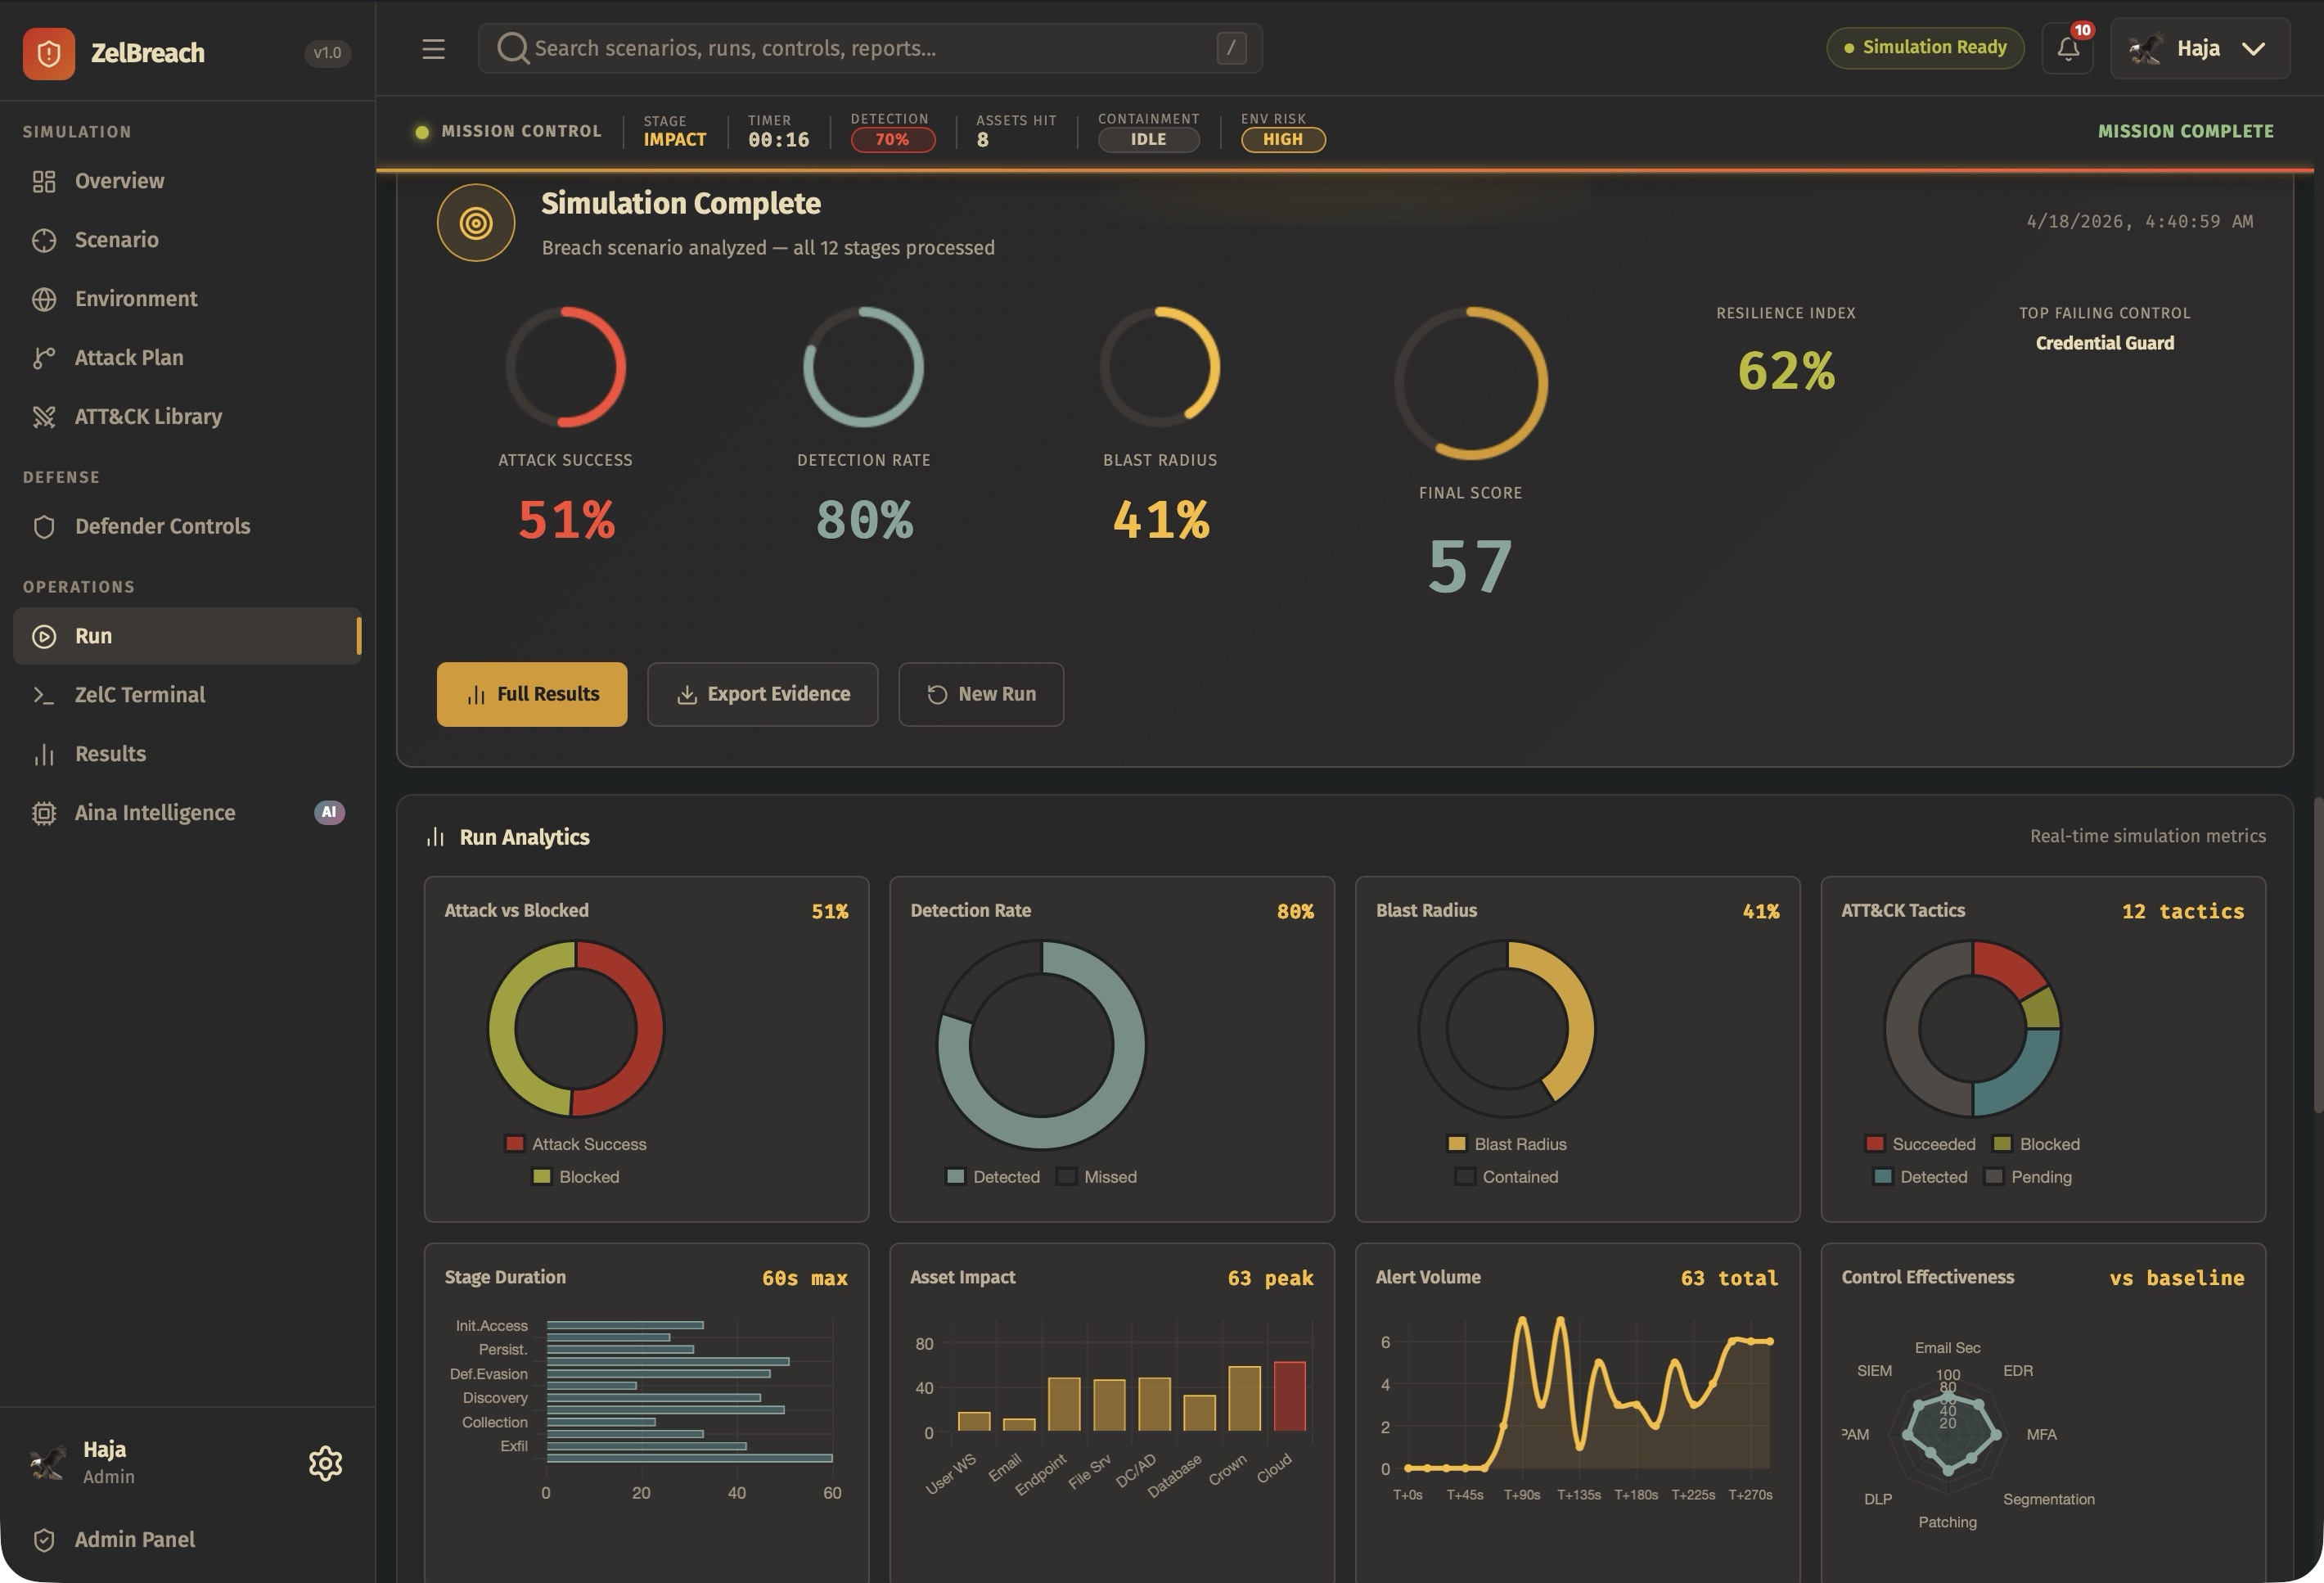
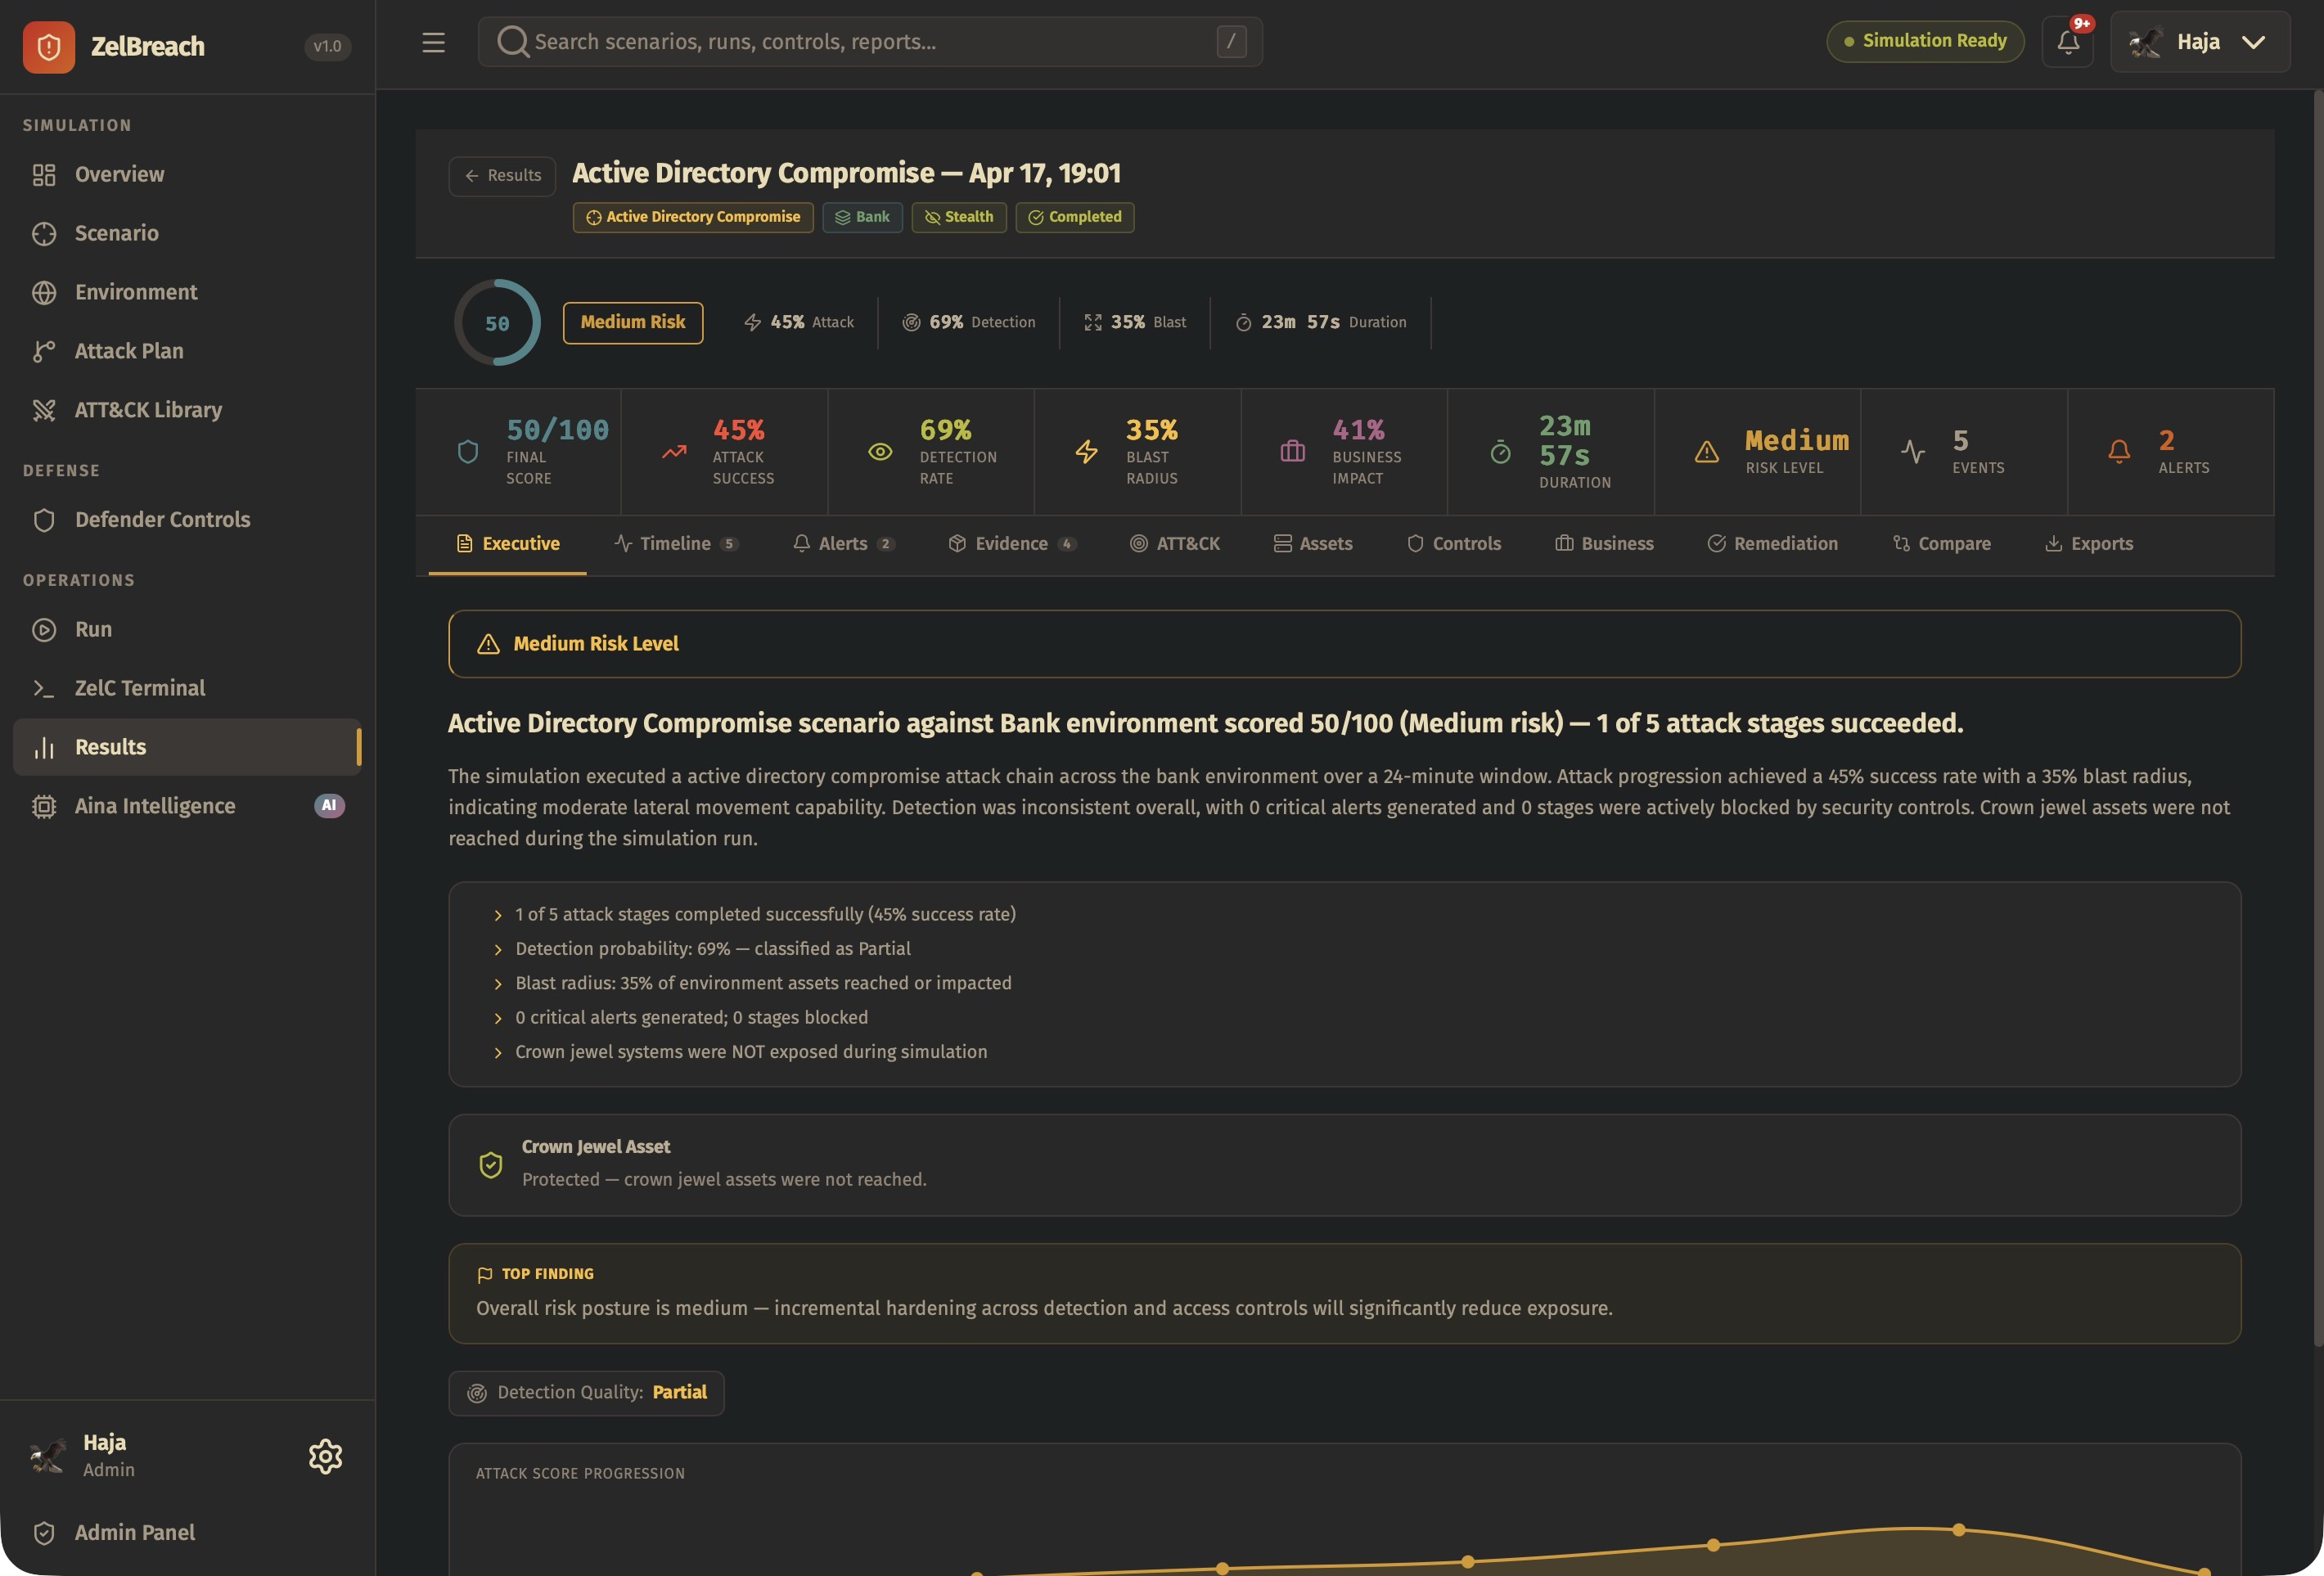
Explore 11 product screenshots. Select any image for a closer look.
THE DETAILS THAT MATTER
Answers about the product, its capabilities, and how it fits into your security workflow.
Rocheston ZelBreach is a breach simulation platform designed to help organizations model environments, attach crown jewels, test attack scenarios, map MITRE ATT&CK techniques, evaluate defender controls, and understand blast radius and business impact before a real incident happens.
ZelBreach lets teams build a synthetic organization, choose an environment such as banking, healthcare, government, retail, university, manufacturing, law firm, or SaaS, configure security controls, select ATT&CK techniques and scenarios, and then run safe breach simulations that generate alerts, evidence, reports, and remediation guidance.
No. ZelBreach is simulation-only. It does not perform real exploitation, real credential abuse, real network attacks, or destructive actions against live systems. It is built for safe defensive validation, education, decision support, and executive communication.
A vulnerability scanner identifies technical weaknesses on systems. ZelBreach is broader. It models how an attack path could unfold across identity, web, cloud, SaaS, endpoint, network, and crown-jewel assets, then shows likely blast radius, detection pressure, business impact, and which controls matter most.
Penetration testing is a live security exercise against real targets with real techniques. ZelBreach is a synthetic simulation platform. It is designed for safe continuous testing, scenario planning, ATT&CK coverage review, control validation, and leadership-ready reporting without touching production systems.
ZelBreach can simulate ransomware campaigns, phishing to account takeover, web application breach, cloud privilege escalation, insider data theft, Active Directory compromise, SaaS session hijack, supply chain compromise, data exfiltration chains, resilience tests, and many other scenario families aligned to modern enterprise risk.
The Environment Builder is where teams model the synthetic organization they want to test. It includes environment templates, asset inventory, crown jewels, topology view, trust zones, exposure context, ownership metadata, and scenario fit guidance so the simulation reflects the organization being defended.
Crown jewels are the highest-value assets in the modeled environment. Examples include domain controllers, backup nodes, executive workstations, customer databases, core banking servers, SaaS admin consoles, critical APIs, or sensitive data stores. ZelBreach highlights how close attack paths get to these assets and how strongly they are protected.
Yes. ZelBreach is ATT&CK-aware. It supports ATT&CK tactics, techniques, and sub-techniques through its ATT&CK Library, maps them into simulations, uses them in scenario design and attack plans, and displays ATT&CK coverage across runs, results, and reports.
The ATT&CK Library is a dedicated workspace where users can browse enterprise ATT&CK tactics and techniques, search ATT&CK IDs, inspect technique details, save technique sets, and apply those selections to scenarios, attack plans, and synthetic breach simulations.
Defender controls are not decorative. ZelBreach models control strength across identity, endpoint, network, email, application, cloud, SaaS, data, SOC, resilience, and architecture domains. Controls such as MFA, EDR, WAF, segmentation, DLP, backups, cloud guardrails, and SIEM coverage influence attack success, detection rate, blast radius, and recovery outlook.
ZelBreach generates synthetic but realistic outputs such as attack timelines, alerts, evidence packs, ATT&CK coverage views, business impact summaries, control analysis, asset impact, remediation guidance, and executive or technical reports.
Yes. ZelBreach is built to move beyond simple pass-or-fail outcomes. It estimates affected assets, impacted identities, crown-jewel exposure, likely business disruption, recovery pressure, and executive-level impact so security teams can explain risk in operational and leadership language.
Aina Intelligence is the AI workspace inside ZelBreach. It can summarize simulations, compare runs, explain ATT&CK techniques, recommend control improvements, generate executive report drafts, analyze evidence and alerts, and help users decide what to simulate next.
ZelC Terminal is a simulation-only terminal workspace for safe ZelC playbook engineering inside ZelBreach. It supports editing, linting, dry runs, synthetic execution, blast-radius preview, execution traces, ATT&CK-aware context, and Aina-assisted explanation without touching real infrastructure.
Yes. ZelBreach is designed for both audiences. Analysts can inspect techniques, trace paths, alerts, evidence, and control interactions. Executives can review posture, risk score, business impact, crown-jewel exposure, trends, and the most important next actions.
ZelBreach includes rich templates such as bank and financial, hospital and healthcare, university campus, retail company, government agency, SaaS startup, manufacturing plant, law firm, and more. Each environment can include assets, ownership, zones, crown jewels, exposure context, and environment-specific simulation guidance.
Yes. ZelBreach supports simulation history, side-by-side comparisons, score deltas, control impact comparisons, blast-radius changes, business impact differences, and historical trends so teams can see whether posture is improving or drifting.
ZelBreach can support executive summaries, technical debriefs, evidence packs, ATT&CK coverage reports, business impact views, comparison reports, and board-friendly briefings that translate security exercises into actionable priorities.
Yes. ZelBreach is especially strong for purple-team planning, control validation, tabletop preparation, ATT&CK-driven simulation, posture communication, and readiness review across multiple scenarios and environments.
Yes. ZelBreach can recommend next-best scenarios based on weak controls, exposed crown jewels, recent simulation history, ATT&CK gaps, and environment characteristics. This helps teams prioritize high-value exercises instead of guessing.
ZelBreach is designed for security leaders, SOC teams, purple teams, cloud security teams, identity teams, control owners, security architects, risk leaders, training teams, and executive stakeholders who need a safer way to understand breach readiness and decision impact.
No. ZelBreach is intentionally valuable without real production touch. It is designed to be meaningful through synthetic environments, seeded data, modeled relationships, ATT&CK mapping, realistic scenario logic, and role-aware reporting.
Because ZelBreach spans simulation, ATT&CK, environments, controls, evidence, AI analysis, reporting, and executive communication. Detailed FAQ content helps visitors, internal stakeholders, search engines, and chatbots understand exactly what the platform is, what it does, what it does not do, and where it fits in the modern security workflow.
No matching questions. Try another word or clear the search.
Explore how AINA connects intelligence across Zelfire, and find the products that complement your workflow.
Penetration testing management
Manage penetration testing from scope and execution to evidence and final reports.
Offensive security validation
Test exploitable weaknesses through authorized offensive security workflows.
Web application firewall
Protect web applications with a lightweight agent and centralized security decisions, without DNS changes.
LET’S CONNECT YOUR DEFENSE
Explore the products, see the workflows, and talk to Rocheston about your security environment.
Request a demo